crowdsec

crowdsecurityMIT活跃维护

开源的入侵检测与防御系统,兼做 WAF 和机器人识别,靠社区共享的恶意 IP 黑名单帮你在 Linux、Windows、容器和 K8s 上自动封禁攻击源。

Open-source IDS/IPS, WAF and bot detection for Linux, Windows, Docker and Kubernetes, with a crowdsourced blocklist of malicious IPs.

v1.8.2发布于 2026-10-26 14:16 UTC15,525star +28 / 7 天758fork同步于 2026-11-10 05:26 UTC

怎么上手

README 里没有找到可直接复制的安装命令

README 里没有找到可直接复制的安装命令,请到 README 或官方文档查看安装方式。

硬件要求

README 没有说明硬件要求。

下载:源码 zip·GitHub Releases(安装包)本站不镜像安装包

项目说明

这个项目的说明还在生成中,先参考下面「最近发版」和 README。

最近发版

5 个版本v1.8.2
  1. v1.8.2最新正式版2026-10-26 · 2026-10-26 14:16 UTC

    Version 1.8.2

    • Brings custom JS fingerprinting capabilities to the bot detection feature, allowing both users and us to distribute detection rules directly via the hub.
    • Brings rate limiting feature to the WAF.
    • Brings performance improvements to the Security Engine, optimizing both memory copy behaviors and relying on static analysis to avoid processing unnecessary regular expressions.
    • Brings performance improvements to the WAF, optimizing out-of-band rules processing.
    • Brings performance improvements to the Bot Detection, optimizing memory usage.

    New Features & Major improvements

    • [WAF] Add RateLimiting feature (#4721) @blotus
    • [bot-detection] Add custom JS fingerprinting capabilities (#4657) @buixor
    • [bot-detection] Add cscli bot subcommand (#4666) @blotus
    • [WAF] Improve out-of-band rules performances (#4722) @blotus
    • [Security Engine] Run postoverflows in a separate goroutine to avoid blocking on slow enrichments (#4672) @blotus
    • [bot-detection] Improve memory usage (#4674) @blotus
    • [Security Engine] Various performance improvements to regular expression processing (#4736) (#4731) (#4729) @blotus @buixor

    Improvements

    • Add cs_features metric (#4770) @blotus
    • bot detection: add an option to set SameSite=None + Partitioned flag on cookie (#4764) @blotus
    • exprhelpers: add GetDecisionsSinceCountByScenario (#4756) @tommy-ng0
    • lapi: optionally limit concurrent decision stream requests (#4747) @tommy-ng0
    • exprhelpers: LookupHost goes through the DNS cache (#4741) @twiesing
    • metrics: add CAPI last pull timestamp and error counter (#4749) @NazarkinRoman
    • prometheus: add kind label to cs_alerts (#4742) @blotus
    • lapi: make decisions stream page size configurable (#4733) @tommy-ng0
    • Fix ValidateChallengeResponse (#4737) @buixor
    • bot-detection: add new FlagSubmission() helper (#4727) @blotus
    • appsec: add an optional category to the request score (#4715) @buixor
    • apiserver: reload the TLS server certificate when its files change (#4709) @ohartwig
    • fix image link (#4702) @buixor
    • waf: add SkipProcessing() helper (#4667) @blotus
    • [bot-detection] drop the URI from the cookie (#4656) @buixor

    Bug Fixes

    • acquisition/file: don't send half-written lines, or skip the lines after them (#4678) @n1koo, @blotus, @claude
    • fix(cscli): display human-readable timestamps in local time (#4759) @sep2
    • remove runtime Fatalf calls (#4760) @blotus
    • waf: fix log spam when usin unix socket on freebsd (#4745) @blotus
    • docker: read from now if container restarts (#4605) @blotus
    • splunk-notification: add an option to configure InsecureSkipVerify (#4720) @blotus
    • victorialogs: move the datasource to RestartableStreamer interface (#4738) @blotus
    • metrics: remove series of deleted machines and bouncers (#4712) @somaz94
    • buckets: make a copy of all event maps before pouring the event to a bucket (#4481) @blotus
    • fix(database): keep simulated decisions from suppressing real bans (#4679) @4erdenko, @blotus
    • fix a nasty bug in transfrom where the effective uuid for a datasource (#4697) @sabban
    • hubtest: add a tiebreaker based on the alert date to have a consistent order (#4699) @blotus
    • syslog: copy buffer before handing it to the datasource (#4690) @blotus
    • Expand env vars in online_api_credentials.yaml (#4677) @kushiemoon-dev

    Chore / Deps

    • build(deps): bump the gomod group with 5 updates (#4778) @dependabot[bot]
    • build(deps): bump the github-actions group with 2 updates (#4777) @dependabot[bot]
    • build(deps): bump certifi from 2026.1.4 to 2026.10.19 in /build/docker/test (#4780) @dependabot[bot]
    • build(deps): bump the github-actions group across 1 directory with 8 updates (#4766) [@dependabot[bot]](http
  2. v1.8.2-rc2pre-release2026-10-22 · 2026-10-22 08:51 UTC
    查看更新说明

    Changes

    • AGENTS.md: clearer guidance on tests (#4713) @blotus
    • pimp readme (#4701) @buixor

    New Features

    • waf: add RateLimit() helper (#4721) @blotus
    • [bot-detection] Add custom JS fingerprinting capabilities (#4657) @buixor

    Improvements

    • Add cs_features metric (#4770) @blotus
    • bot detection: add an option to set SameSite=None + Partitioned flag on cookie (#4764) @blotus
    • exprhelpers: add GetDecisionsSinceCountByScenario (#4756) @tommy-ng0
    • lapi: optionally limit concurrent decision stream requests (#4747) @tommy-ng0
    • exprhelpers: LookupHost goes through the DNS cache (#4741) @twiesing
    • metrics: add CAPI last pull timestamp and error counter (#4749) @NazarkinRoman
    • add cscli bot subcommand (#4666) @blotus
    • prometheus: add kind label to cs_alerts (#4742) @blotus
    • lapi: make decisions stream page size configurable (#4733) @tommy-ng0
    • Fix ValidateChallengeResponse (#4737) @buixor
    • grok: only keep capture groups that can be accessed in evt.Parsed (#4736) @blotus
    • grokky : preshot static strings (#4731) @buixor, @Copilot
    • grokky : ParseInto (#4729) @buixor
    • bot-detection: add new FlagSubmission() helper (#4727) @blotus
    • appsec: add an optional category to the request score (#4715) @buixor
    • apiserver: reload the TLS server certificate when its files change (#4709) @ohartwig
    • fix image link (#4702) @buixor
    • waf: add SkipProcessing() helper (#4667) @blotus
    • [bot-detection] drop the URI from the cookie (#4656) @buixor

    Bug Fixes

    • fix RateLimit() tests (#4771) @blotus
    • database: match the alert ip/range filter on a single decision (#4710) @AdzerKI
    • acquisition/file: don't send half-written lines, or skip the lines after them (#4678) @n1koo, @blotus, @claude
    • fix(cscli): display human-readable timestamps in local time (#4759) @sep2
    • waf: use dedicated workers for OOB processing (#4722) @blotus
    • remove runtime Fatalf calls (#4760) @blotus
    • waf: fix log spam when usin unix socket on freebsd (#4745) @blotus
    • docker: read from now if container restarts (#4605) @blotus
    • splunk-notification: add an option to configure InsecureSkipVerify (#4720) @blotus
    • victorialogs: move the datasource to RestartableStreamer interface (#4738) @blotus
    • metrics: remove series of deleted machines and bouncers (#4712) @somaz94
    • postoverflow: run them in a goroutine to not block writers, enforce max in-flight alerts, and warn if queue is becoming too full (#4672) @blotus
    • buckets: make a copy of all event maps before pouring the event to a bucket (#4481) @blotus
    • fix(database): keep simulated decisions from suppressing real bans (#4679) @4erdenko, @blotus
    • fix a nasty bug in transfrom where the effective uuid for a datasource (#4697) @sabban
    • hubtest: add a tiebreaker based on the alert date to have a consistent order (#4699) @blotus
    • challenge: optimize memory usage (#4674) @blotus
    • syslog: copy buffer before handing it to the datasource (#4690) @blotus
    • Expand env vars in online_api_credentials.yaml (#4677) @kushiemoon-dev

    Chore / Deps

    • build(deps): bump the github-actions group across 1 directory with 8 updates (#4766) @dependabot[bot]
    • build(deps): bump the gomod group with 16 updates (#4767) @dependabot[bot]
    • build(deps): bump the gomod group with 8 updates (#4753) @dependabot[bot]
    • fpscanner: use fork (#4761) @blotus
    • waf: update to coraza 3.8.0 (#4724) @blotus, @buixor
    • build(deps): bump the gomod group across 1 directory with 19 updates (#4730) @dependabot[bot]
    • CI: skip more docker tests on windows (#4728) @blotus
    • grok: embed grok library instead of having it as a dep (#4725) @blotus
    • docker datasource: skip tests on windows (#4719) @blotus
    • agents.md: keep comments to a reasonable level (#4716) @blotus
    • build(deps): bump the github-actions group with 7 updates (#4
  3. v1.8.2-rc1pre-release2026-10-13 · 2026-10-13 14:40 UTC
    查看更新说明

    Changes

    • AGENTS.md: clearer guidance on tests (#4713) @blotus
    • pimp readme (#4701) @buixor

    New Features

    • [bot-detection] Add custom JS fingerprinting capabilities (#4657) @buixor

    Improvements

    • exprhelpers: LookupHost goes through the DNS cache (#4741) @twiesing
    • metrics: add CAPI last pull timestamp and error counter (#4749) @NazarkinRoman
    • add cscli bot subcommand (#4666) @blotus
    • prometheus: add kind label to cs_alerts (#4742) @blotus
    • lapi: make decisions stream page size configurable (#4733) @tommy-ng0
    • Fix ValidateChallengeResponse (#4737) @buixor
    • grok: only keep capture groups that can be accessed in evt.Parsed (#4736) @blotus
    • grokky : preshot static strings (#4731) @buixor, @Copilot
    • grokky : ParseInto (#4729) @buixor
    • bot-detection: add new FlagSubmission() helper (#4727) @blotus
    • appsec: add an optional category to the request score (#4715) @buixor
    • apiserver: reload the TLS server certificate when its files change (#4709) @ohartwig
    • fix image link (#4702) @buixor
    • waf: add SkipProcessing() helper (#4667) @blotus
    • [bot-detection] drop the URI from the cookie (#4656) @buixor

    Bug Fixes

    • waf: fix log spam when usin unix socket on freebsd (#4745) @blotus
    • docker: read from now if container restarts (#4605) @blotus
    • splunk-notification: add an option to configure InsecureSkipVerify (#4720) @blotus
    • victorialogs: move the datasource to RestartableStreamer interface (#4738) @blotus
    • metrics: remove series of deleted machines and bouncers (#4712) @somaz94
    • postoverflow: run them in a goroutine to not block writers, enforce max in-flight alerts, and warn if queue is becoming too full (#4672) @blotus
    • buckets: make a copy of all event maps before pouring the event to a bucket (#4481) @blotus
    • fix(database): keep simulated decisions from suppressing real bans (#4679) @4erdenko, @blotus
    • fix a nasty bug in transfrom where the effective uuid for a datasource (#4697) @sabban
    • hubtest: add a tiebreaker based on the alert date to have a consistent order (#4699) @blotus
    • challenge: optimize memory usage (#4674) @blotus
    • syslog: copy buffer before handing it to the datasource (#4690) @blotus
    • Expand env vars in online_api_credentials.yaml (#4677) @kushiemoon-dev

    Chore / Deps

    • waf: update to coraza 3.8.0 (#4724) @blotus, @buixor
    • build(deps): bump the gomod group across 1 directory with 19 updates (#4730) @dependabot[bot]
    • CI: skip more docker tests on windows (#4728) @blotus
    • grok: embed grok library instead of having it as a dep (#4725) @blotus
    • docker datasource: skip tests on windows (#4719) @blotus
    • agents.md: keep comments to a reasonable level (#4716) @blotus
    • build(deps): bump the github-actions group with 7 updates (#4693) @dependabot[bot]
    • build(deps): bump the gomod group with 11 updates (#4694) @dependabot[bot]
    • build(deps): bump github.com/go-openapi/validate from 0.26.5 to 1.0.0 (#4682) @dependabot[bot]
    • build(deps): bump the gomod group with 19 updates (#4681) @dependabot[bot]
    • build(deps): bump cryptography from 48.0.1 to 50.0.0 in /build/docker/test (#4591) @dependabot[bot]
    • bump to go 1.27 (#4675) @blotus
    • build(deps): bump the github-actions group across 1 directory with 3 updates (#4658) @dependabot[bot]
    • build(deps): bump the gomod group across 1 directory with 21 updates (#4659) @dependabot[bot]

    Geolite2 notice

    This product includes GeoLite2 data created by MaxMind, available from https://www.maxmind.com.

    Installation

    Take a look at the installation instructions.

  4. v1.8.12026-09-03 · 2026-09-03 09:08 UTC
    查看更新说明

    This release fixes a false positive in the bot detection feature for Brave Browser with shields enabled.

    Changes

    Improvements

    • add HasValidChallengeCookie() helper (#4648) @blotus

    Bug Fixes

    • lapi: return an empty slice instead of null when querying alerts (#4653) @blotus
    • challenge: tolerate strings instead of struct in FP payload (#4655) @blotus

    Geolite2 notice

    This product includes GeoLite2 data created by MaxMind, available from https://www.maxmind.com.

    Installation

    Take a look at the installation instructions.

  5. v1.8.02026-08-31 · 2026-08-31 11:09 UTC
    查看更新说明

    Bot detection with CrowdSec WAF

    This release brings a major change to the CrowdSec WAF: a bot detection feature.

    If enabled, clients will be served a challenge + fingerprinting page before accessing the website. CrowdSec will evaluate the challenge and check the fingerprint against pre-configured rules to decide whether the client looks legitimate or not.

    You can find more information about this new feature in the documentation.

    Other notable changes include:

    • A dedicated kubernetes datasource: crowdsec will fetch logs directly from the k8s apiserver
    • New HTTP helpers for the expression language, to query external services from parsers and scenarios
    • Performance improvements on the decisions stream endpoint in LAPI

    Security Notice

    This release fixes 2 denial of service vulnerabilities in the HTTP and k8s-audit datasources:

    • HTTP acquisition datasource lacks a decompressed body cap and trusts Content-Length: GHSA-g2x2-jgfg-pg7g
    • Unbounded request-body read in kubernetes-audit acquisition webhook: GHSA-rh69-4vqj-9gj8

    New Features

    • k8s log acquisition datasource (#4221) @sabban
    • Waf challenge mode (#4268) @blotus

    Improvements

    • challenge: detect if cookies are disabled and display an explicit error message (#4628) @blotus
    • db: add composite index for decision dedup (#4619) @blotus
    • Improve pow solving : optimize & increase difficulty (#4617) @buixor
    • Bot detection unify scores (#4608) @buixor
    • Dedup code reject submission alert generation (#4606) @buixor
    • make RejectSubmission generate an alert (#4602) @buixor
    • waf challenge: add threshold support (#4593) @blotus
    • revamp 'cscli console status' to be all-in-one (#4592) @buixor
    • [bot-detection] Fix leak of background pre-warmer goroutine (#4589) @buixor
    • waf: allow to configure auth timeout to LAPI (#4585) @blotus
    • Add cs_machines_heartbeat_seconds metric (#4569) @kushiemoon-dev
    • Cscli hub list improvements (#4567) @buixor
    • expr: add HTTP helpers (#4533) @blotus

    Bug Fixes

    • leakybuckets: make alerts own their strings (#4643) @blotus
    • alerts: create metas only if alert was not discarded (#4633) @blotus
    • k8s-audit: add support for max body size (#4630) @blotus
    • Usage metrics: set a maximum payload size (#4629) @blotus
    • lapi: use decision id as cursor for delta pull (#4620) @blotus
    • acquis(http): Set default max body size and enforce it as well for compressed streams (#4616) @blotus
    • acquisition: fix transformation being ignored (#4609) @blotus
    • fpscanner: add missing fields (#4604) @blotus
    • docs: fix broken Vagrant include link in test README (#4594) @latent-9
    • challenge: require SSE4.1 + WX memory (#4590) @blotus
    • WAF: supress erroneous warnings/errors when loading config / no rule has matched (#4587) @blotus
    • Bot Detection: keep the original URL in the generated alert (#4586) @buixor
    • fix(docker): allow spaces in ENROLL_INSTANCE_NAME (#4582) @sahilnyk
    • apiclient: return nil response if we couldnt connect to LAPI (#4573) @blotus
    • cscli lapi register: no error if the credentials file does not exist (#4570) @lopster568
    • fix(docker): avoid panic on colliding nested crowdsec labels (#4555) @arpitjain099
    • fix(syslog): don't close the shared acquisition output channel (#4553) @alxrxs
    • waf: track id/name pairs for all subrules (#4505) @blotus
    • apiserver: prevent from fetching JWT token from query string (#4554) @blotus
    • fix(leakybucket): emit overflow before pouring the next event (#4547) @blotus
    • loki: prevent duplicate log ingestion and improve timestamp handling (#4498) @Anulo2
    • db: use proper mutex when checking if flush can happen (#4528) @blotus
    • db: do not flush alerts with active decisions (#4527) @blotus
    • Fix

用户点评

登录用户的真实使用记录,可按版本和硬件筛选
共 0 条

    还没有人点评。第一个说出真实体验的人最有价值。

    README 原文

    未翻译

    CrowdSec is an open-source and participative security solution offering crowdsourced server detection and protection against malicious IPs. Detect and block with our Security Engine, contribute to the network, and enjoy our real-time community blocklist.

    Features & Advantages

    Versatile Security Engine

    CrowdSec Security Engine is an all-in-one IDS/IPS and WAF.

    It detects bad behaviors by analyzing log sources and HTTP requests, and allows active remediation thanks to the Remediation Components.

    Detection rules are available on our hub under MIT license.

    CrowdSec Community Blocklist

    The "Community Blocklist" is a curated list of IP addresses identified as malicious by CrowdSec. The Security Engine proactively blocks the IP addresses of this blocklist, preventing malevolent IPs from reaching your systems.
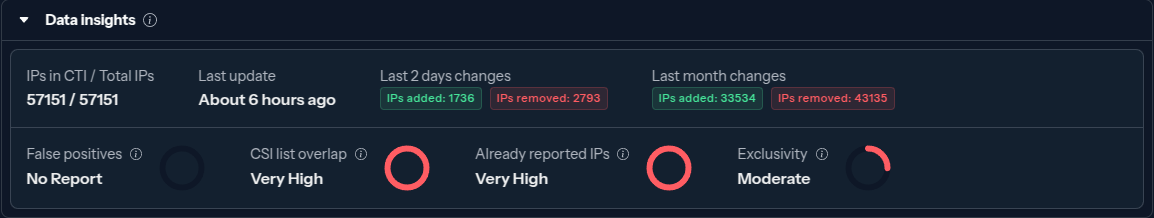
    CrowdSec Community Blocklist

    Console - Monitoring & Automation of your security stack
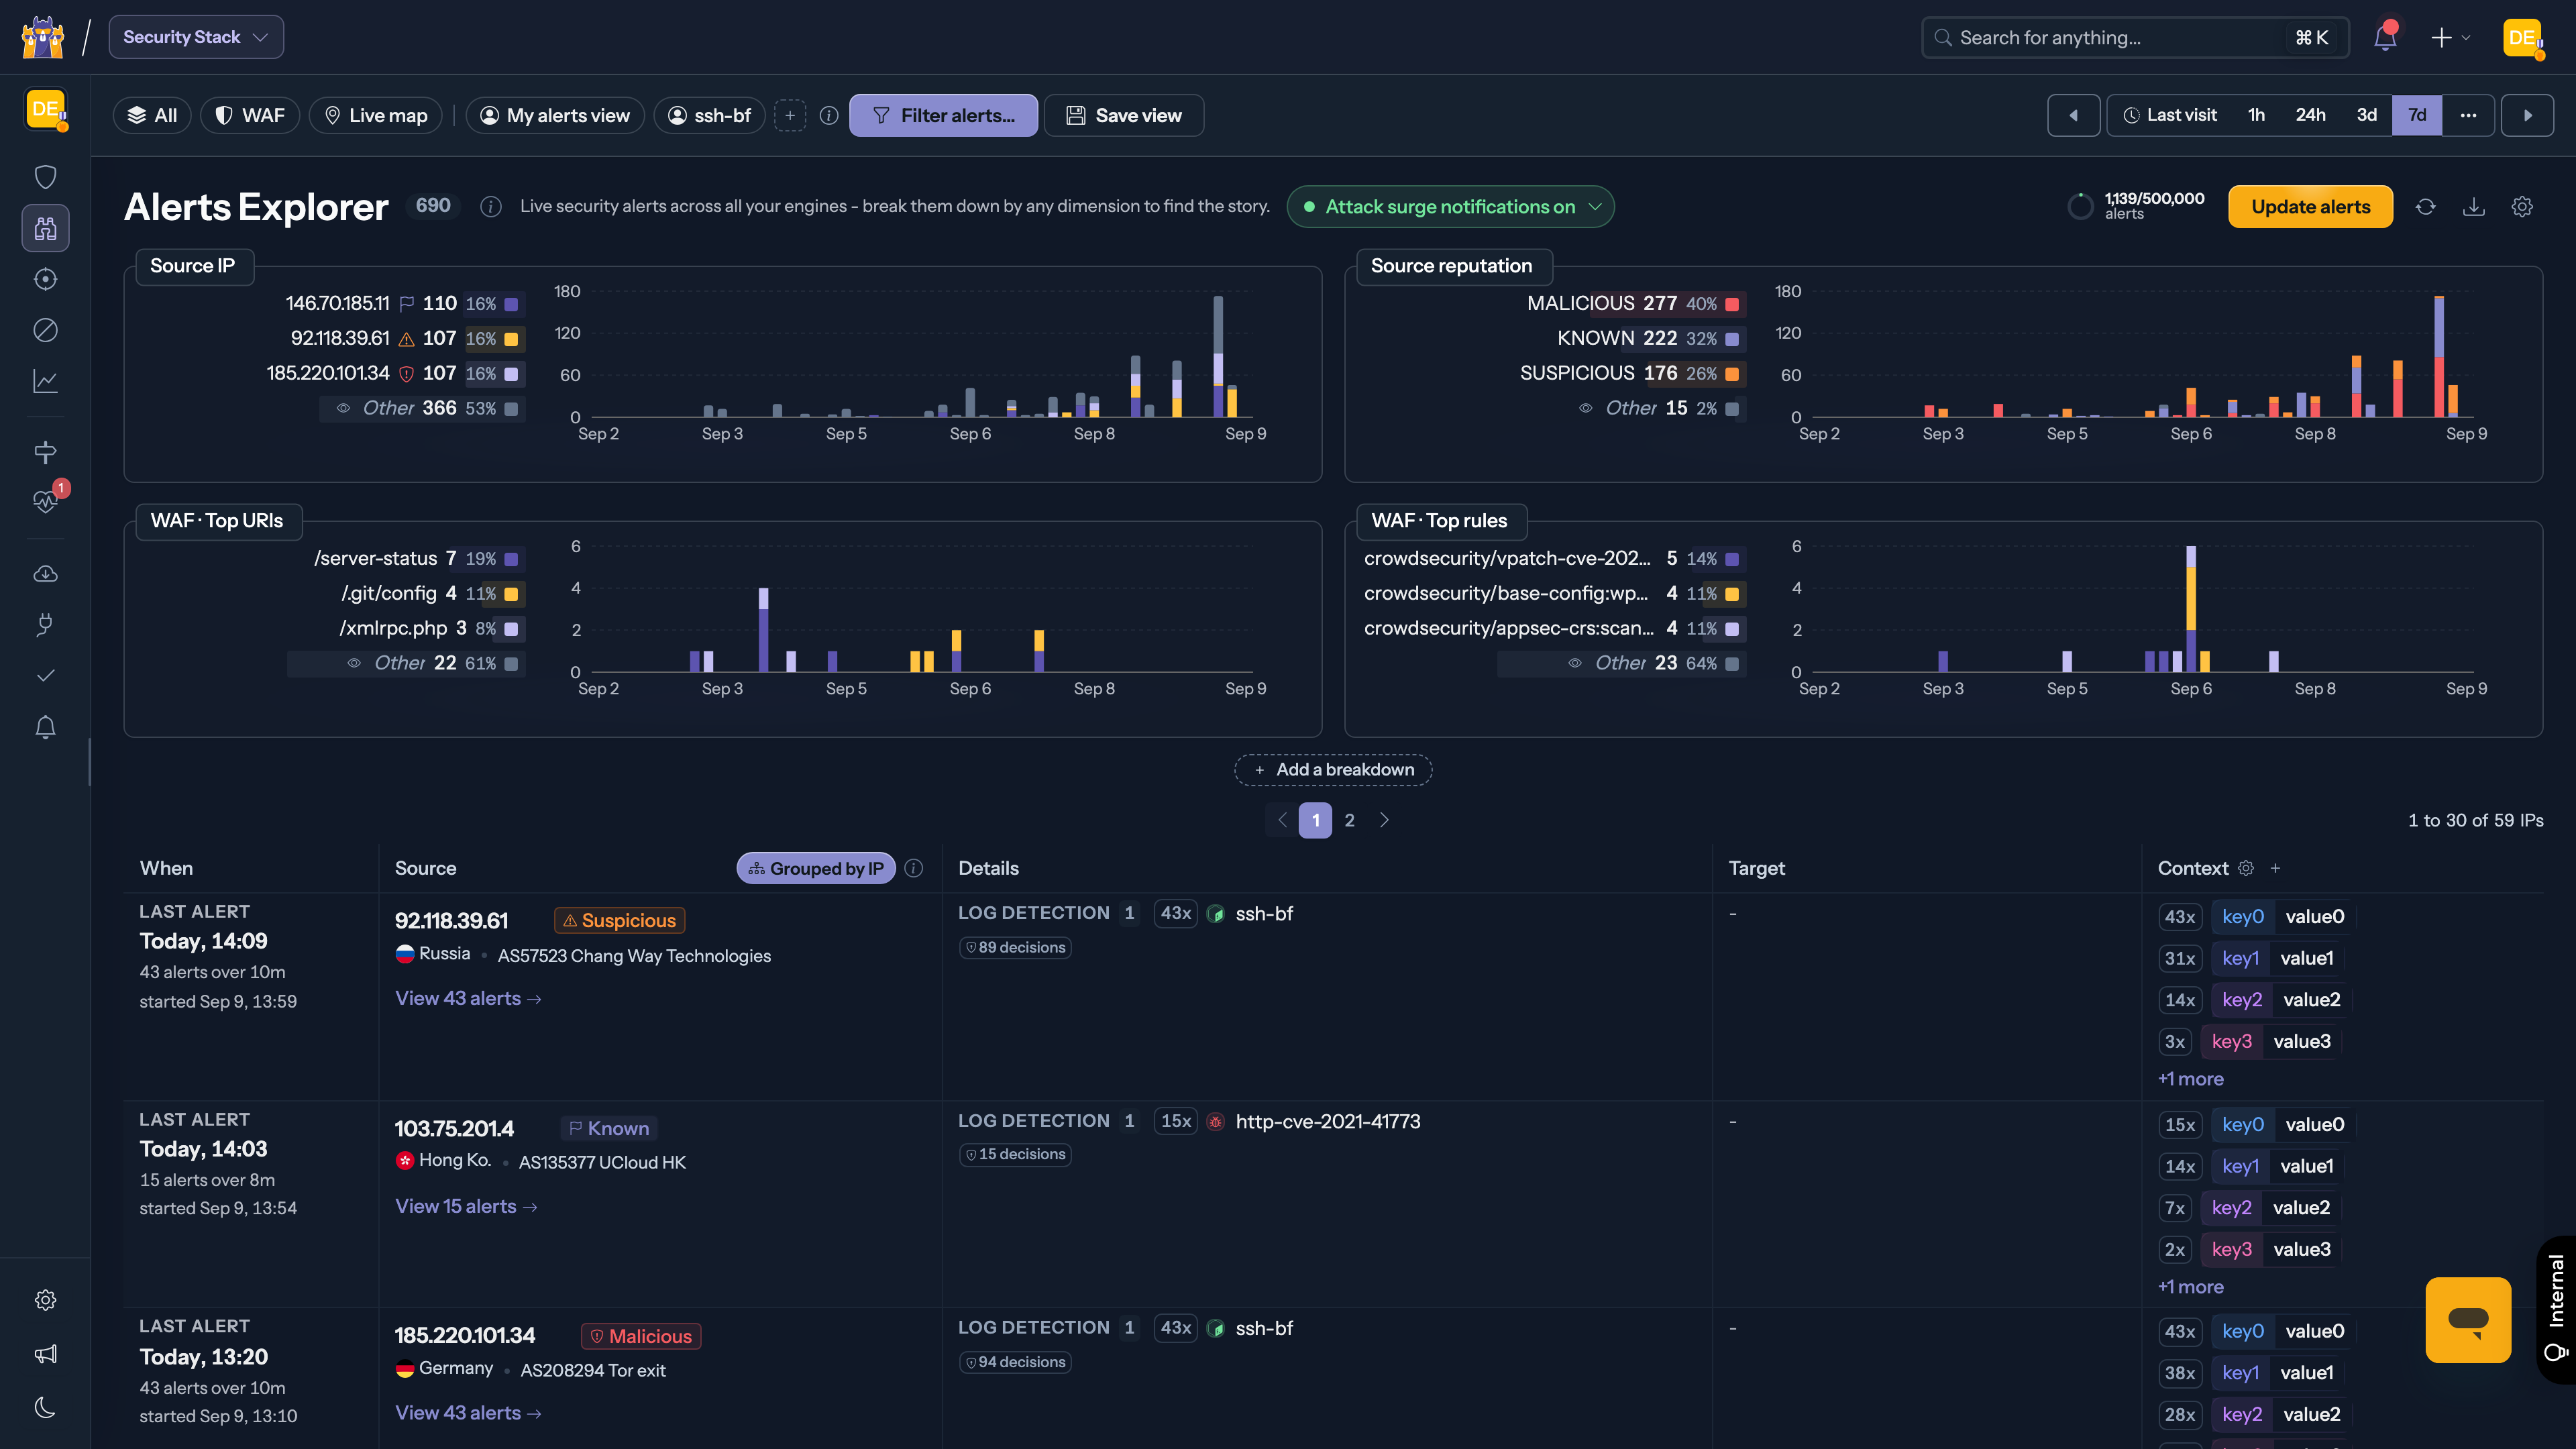
    CrowdSec Console

    Multiple Platforms support

    Multiple Platforms support

    How CrowdSec compares

    To fail2ban — CrowdSec reads the same log files and bans the same IPs, but detection and remediation are decoupled: parse logs on one machine, block at the firewall, reverse proxy or CDN on another. Attacks you report feed a community blocklist, so an IP that hits one user gets blocked for everyone else before it reaches them.

    To ModSecurity, Coraza and naxsi — the AppSec component is a WAF built on Coraza, so SecLang rules and the OWASP Core Rule Set load as-is. On top of that it adds a YAML rule format, and shares the IP reputation and remediation layer with the log-based engine.

    Bot and scraper detection — AppSec can answer a suspicious request with a JavaScript proof-of-work challenge at a tunable difficulty, which stops headless browsers and scrapers while letting verified crawlers such as Googlebot through.

    Outnumbering hackers all together

    By sharing the threat they faced, all users are protecting each other (hence the name Crowd-Security). Crowdsec is designed for modern infrastructures, with its "Detect Here, Remedy There" approach, letting you analyze logs coming from several sources in one place and block threats at various levels (applicative, system, infrastructural) of your stack.

    CrowdSec ships by default with scenarios (brute force, port scan, web scan, etc.) adapted for most contexts, but you can easily extend it by picking more of them from the HUB. It is also easy to adapt an existing one or create one yourself.

    Installation

    Follow our documentation to install CrowdSec in a few minutes on Linux, Windows, Docker, OpnSense, Kubernetes, and more.

    Resources

    • Console: Supercharge your CrowdSec setup with visualization, management capabilities, extra blocklists and premium features.
    • Documentation: Learn how to exploit your CrowdSec setup to deter more attacks.
    • Discord: A question or a suggestion? This is the place.
    • Hub: Improve your stack protection, find the relevant remediation components for your infrastructure.
    • Public Roadmap: Vote for your favorite features and submit ideas to influence what we build next.
    • CrowdSec Academy: Learn and grow with our courses.
    • Corporate Website: For everything else.