README 未给出具体安装命令,需按官方文档操作;不同部署方式(Docker Compose、Kubernetes、AWS)需分别参考对应文档
authentik
goauthentik活跃维护开源身份认证平台,把 OAuth2、OIDC、SAML 和反向代理认证统一到一套系统里,帮团队给自建应用和 K8s 服务快速接上单点登录和权限控制。
The authentication glue you need.
version/2026.8.5发布于 2026-10-21 12:57 UTC26,290star +26 / 7 天2,122fork同步于 2026-11-10 11:22 UTC
Docker Compose 部署请参考 https://docs.goauthentik.io/docs/install-config/install/docker-compose/ 硬件要求按 README 说明
README 未说明
有 Docker 镜像
开源身份提供者,自托管统一 SSO,替代 Okta、Auth0 等商业 IdP
开源身份认证平台,把 OAuth2、OIDC、SAML 和反向代理认证统一到一套系统里,帮团队给自建应用和 K8s 服务快速接上单点登录和权限控制。
核心能力
- 支持 SAML、OAuth2/OIDC、LDAP、RADIUS 等多种协议
- 可自托管,覆盖从小型实验环境到大型生产集群
- 提供 Docker Compose、Kubernetes Helm、AWS CloudFormation 等部署方式
- 提供企业版,可替换 Okta、Auth0、Entra ID、Ping Identity
容易踩的坑
内容由模型根据 README 生成,可能不完整或不准确,以官方文档为准。看原文 README
- version/2026.8.5Release 2026.8.5最新正式版2026-10-21 · 2026-10-21 12:57 UTC
See https://docs.goauthentik.io/docs/releases/2026.8#fixed-in-202685
What's Changed
- endpoints: fix MultipleObjectsReturned (cherry-pick #26971 to version-2026.8) (#26972)
- enterprise/providers/microsoft_entra: skip members already in the group (cherry-pick #26891 to version-2026.8) (#26952)
- root: bump cert-related deps due to emudhra (cherry-pick #27068 to version-2026.8) (#27071)
- web/stages: Fix stage type errors (cherry-pick #25689 to version-2026.8) (#26194)
- web/user: fix agents tab flashing without license (cherry-pick #27069 to version-2026.8) (#27073)
Full Changelog: https://github.com/goauthentik/authentik/compare/version/2026.8.4...version/2026.8.5
- version/2026.5.8Release 2026.5.82026-10-21 · 2026-10-21 12:55 UTC
查看更新说明
See https://docs.goauthentik.io/docs/releases/2026.5#fixed-in-202658
What's Changed
- ci: remove the Google Chrome apt source in setup (cherry-pick #25990 to version-2026.5) by @authentik-cherry-pick[bot] in https://github.com/goauthentik/authentik/pull/26011
- lib/expression: fix PickleError due to resolver match when using ak_call_policy (cherry-pick #25763 to version-2026.5) by @authentik-cherry-pick[bot] in https://github.com/goauthentik/authentik/pull/26071
- web/source/flows: fix flicker after webauthn (cherry-pick #25454 to version-2026.5) by @authentik-cherry-pick[bot] in https://github.com/goauthentik/authentik/pull/25835
- core: bump rustls (cherry-pick #26142 to version-2026.5) by @authentik-cherry-pick[bot] in https://github.com/goauthentik/authentik/pull/26144
- website: add umami (cherry-pick #26460 to version-2026.5) by @authentik-cherry-pick[bot] in https://github.com/goauthentik/authentik/pull/26462
- packages/django-channels-postgres: refresh pool credentials on connection attempts (cherry-pick #26505 to version-2026.5) by @authentik-cherry-pick[bot] in https://github.com/goauthentik/authentik/pull/26549
- web/flows: check if localStorage is available for continuous login (cherry-pick #26267 to version-2026.5) by @authentik-cherry-pick[bot] in https://github.com/goauthentik/authentik/pull/26639
- root: don't fail websocket connections with non-UTF-8 headers (cherry-pick #26688 to version-2026.5) by @authentik-cherry-pick[bot] in https://github.com/goauthentik/authentik/pull/26707
- stages/consent: fix integrity error when re-consenting after consent expired (cherry-pick #26866 to version-2026.5) by @authentik-cherry-pick[bot] in https://github.com/goauthentik/authentik/pull/26871
- ci: switch version bump to action, like platform repo (cherry-pick #26949 to version-2026.5) by @authentik-cherry-pick[bot] in https://github.com/goauthentik/authentik/pull/26951
- root: bump cert-related deps due to emudhra (cherry-pick #27068 to version-2026.5) by @authentik-cherry-pick[bot] in https://github.com/goauthentik/authentik/pull/27070
Full Changelog: https://github.com/goauthentik/authentik/compare/version/2026.5.7...version/2026.5.8
- version/2026.8.4Release 2026.8.42026-10-14 · 2026-10-14 22:53 UTC
查看更新说明
See https://docs.goauthentik.io/docs/releases/2026.8#fixed-in-202684
What Changed in 2026.8.4
- common/saml: Fix metadata to serve only the leaf of a PEM chain (#26273)
- core: handle overflow in duration validation (#26680)
- endpoints: fix error during device lookup with one identifier missing (#26902)
- endpoints: retain last fact snapshot (#26343)
- enterprise/requests: show message after successful request (#26587)
- events: fix group membership changes with OSS audit middleware (#26477)
- flows: allow unauthenticated flows for re-authentication (#26785)
- lifecycle: fix AWS cloudformation template defaults (#26807)
- outposts/proxy: don't negotiate HTTP/2 to upstreams (#26281)
- outposts/proxy: fetch embedded JWKS over the unix socket, not the browser host (#26448)
- outposts/proxy: use HTTP/1.1 for OAuth backchannel requests (#26422)
- packages/ak-axum/extract/client_ip: use the leftmost X-Forwarded-For IP (#26353)
- packages/ak-common/config: fix list values from env variables parsing (#26081)
- packages/django-channels-postgres: refresh pool credentials on connection attempts (#26505)
- providers/proxy: fix startup reconcile not being atomic (#26344)
- providers/scim: accept a service provider that reports bulk as unsupported (#25057)
- providers/scim: fix scim user conflict resolution (#25998)
- providers/scim: show remote error details for 4xx/5xx responses (#26906)
- root, web, docs: revert pnpm to 11.20.0 on version-2026.8 (#26366)
- root: don't fail websocket connections with non-UTF-8 headers (#26688)
- root: fix client certificate header forwarded to the mTLS stage (#26438)
- root: log full stacktrace for ASGI exception (#26415)
- sources/kerberos, sources/ldap: Save source connections when linking an existing user/group (#26059)
- sources/saml: Fallback NameID (#25713)
- stages/consent: fix integrity error when re-consenting after consent expired (#26866)
- web: Close command palette when opening About (#25734)
- web: Fix denied template static form layout. (#26733)
- web: Fix disabled token icon buttons. (#25527)
- web: resolve themed icon URLs everywhere (#25103)
- web/admin: fix device view page and outpost view page (#26383)
- web/admin: restore file upload capability check (#26556)
- web/admin: show agent connector local auth & compliance status (#26610)
- web/admin: update oauth federated provider helptext wording (#26611)
- web/elements: reload edit forms after cancel and on pk change (#26892)
- web/flows: check if localStorage is available for continuous login (#26267)
- web/flows: fix layout shift once initial challenge is loaded (#26758)
- web/user: fix requests banner wording (#26586)
- web/user: remove slug display in any display mode on the user application library page (#26441)
Full Changelog: https://github.com/goauthentik/authentik/compare/version/2026.8.2...version/2026.8.3
- version/2026.8.3Release 2026.8.32026-09-17 · 2026-09-17 22:15 UTC
查看更新说明
See https://docs.goauthentik.io/docs/releases/2026.8#fixed-in-202683
What's Changed
- admin/files: make file search case-insensitive (#25736)
- api: include JSON field relation models in search autocomplete (#26153)
- blueprints: fix
employee_departmenttypo (#26046) - change docker compose to compose (#26087)
- core: fix migrations (version-2026.8) (cherry-pick #26208) (#26209)
- events: Note in logs when an agent makes a call (#26146)
- flows: strip
login_hintfrom next on cancel to prevent loop (#26111) - outposts: refresh sessions when impersonation changes (#26086)
- packages/ak-axum/extract/client_ip: support X-Forwarded-For with ports (#25682)
- policies: fix policybinding cache invalidation (#25989)
- providers/ldap: fix memory leak in the cached searcher (#26028)
- providers/oauth: handle token exchange when no signing key is set (#26049)
- providers/oauth2: only expose URL-based avatars as picture claim (#26080)
- root: document CNA in SECURITY.md (#26124)
- root: fix metric gauges for multiprocessor mode (#25882)
- server: preserve websocket close code when proxying to outposts (#26090)
- sources/saml: Register ID attributes (#25706)
- web/flows: fix hardcoded locale in identification stage's
OR_LIST_FORMATTERS(#26017) - web/scim: Add gitlab compatibility option to form (#26154)
Full Changelog: https://github.com/goauthentik/authentik/compare/version/2026.8.2...version/2026.8.3
- version/2026.8.2Release 2026.8.22026-09-09 · 2026-09-09 19:23 UTC
用户点评
登录用户的真实使用记录,可按版本和硬件筛选共 0 条
还没有人点评。第一个说出真实体验的人最有价值。



What is authentik?
authentik is an open-source Identity Provider (IdP) for modern SSO. It supports SAML, OAuth2/OIDC, LDAP, RADIUS, and more, designed for self-hosting from small labs to large production clusters.
Our enterprise offering is available for organizations to securely replace existing IdPs such as Okta, Auth0, Entra ID, and Ping Identity for robust, large-scale identity management.
Installation
- Docker Compose: recommended for small/test setups. See the documentation.
- Kubernetes (Helm Chart): recommended for larger setups. See the documentation and the Helm chart repository.
- AWS CloudFormation: deploy on AWS using our official templates. See the documentation.
- DigitalOcean Marketplace: one-click deployment via the official Marketplace app. See the app listing.
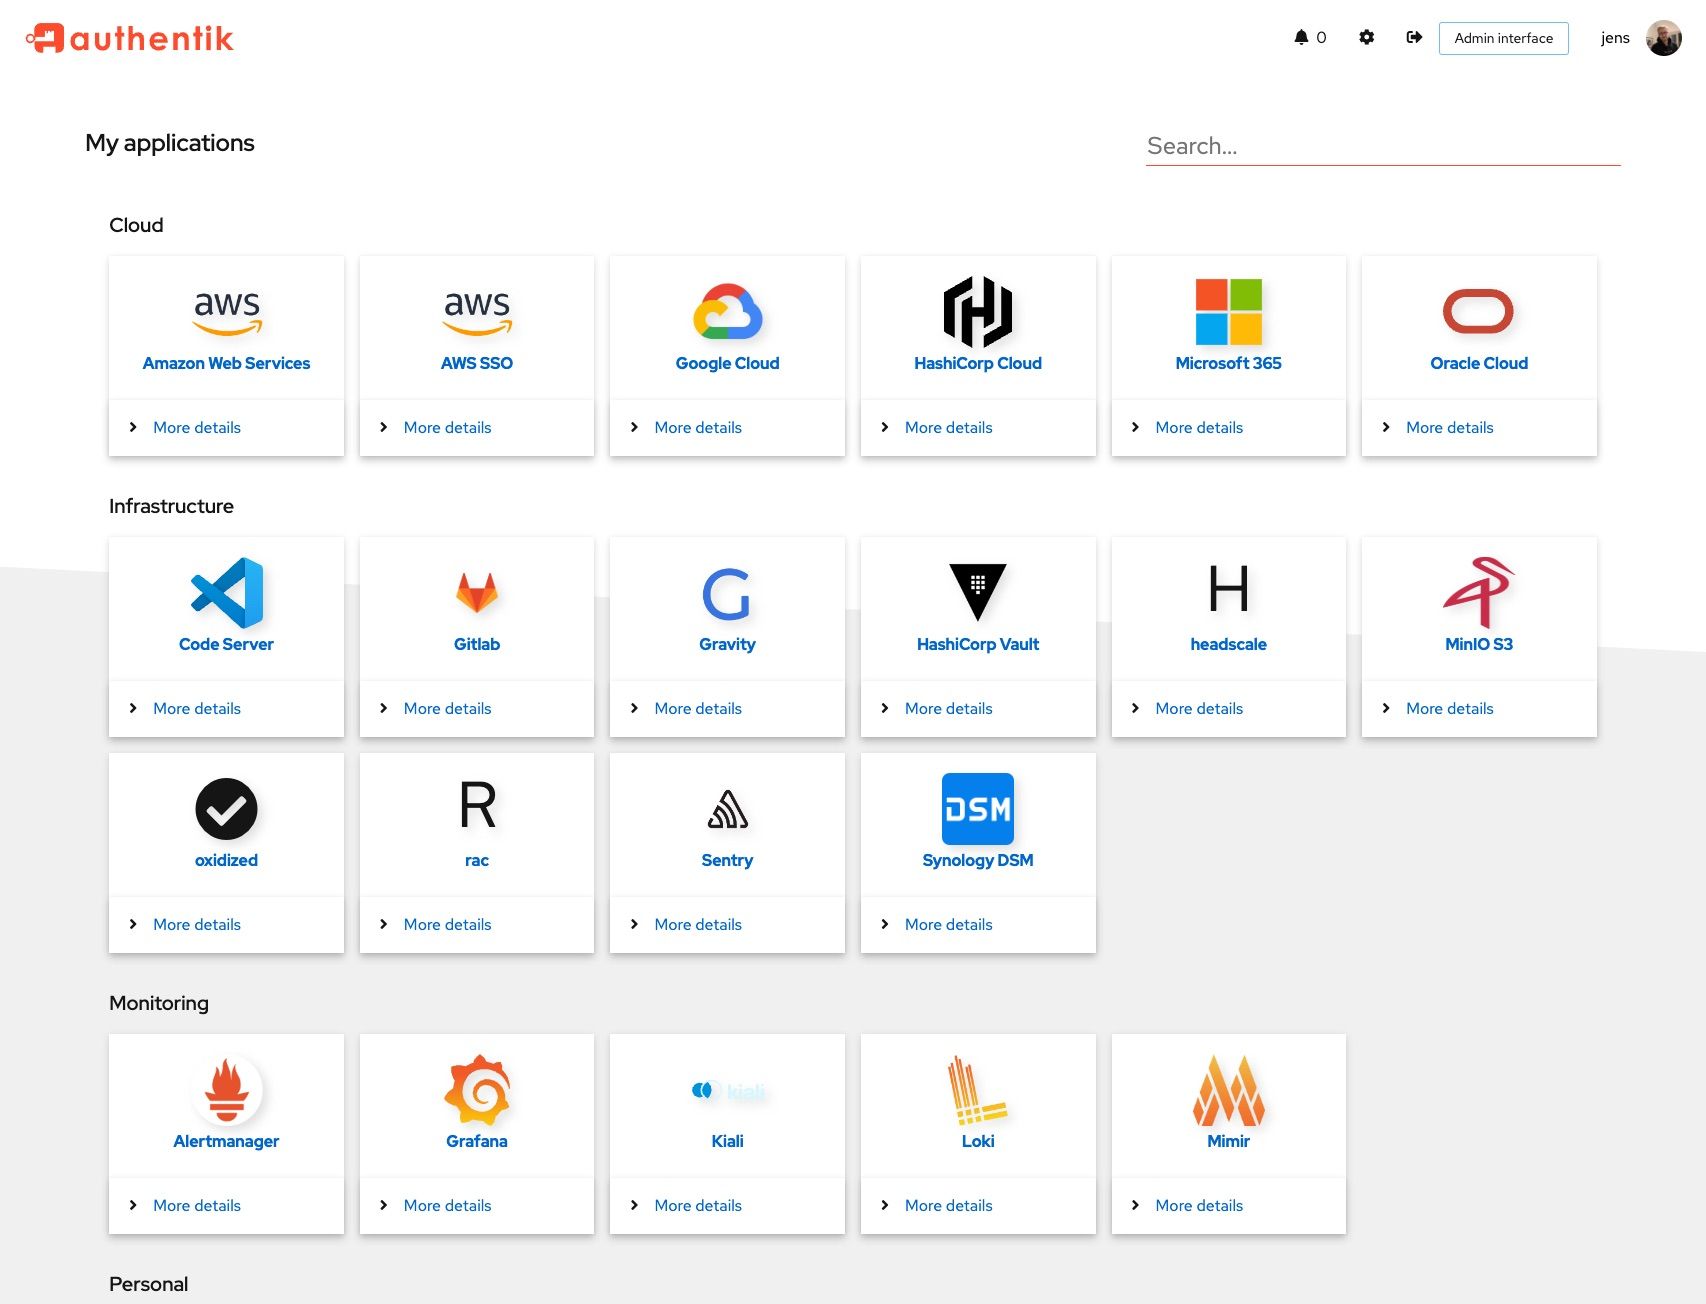
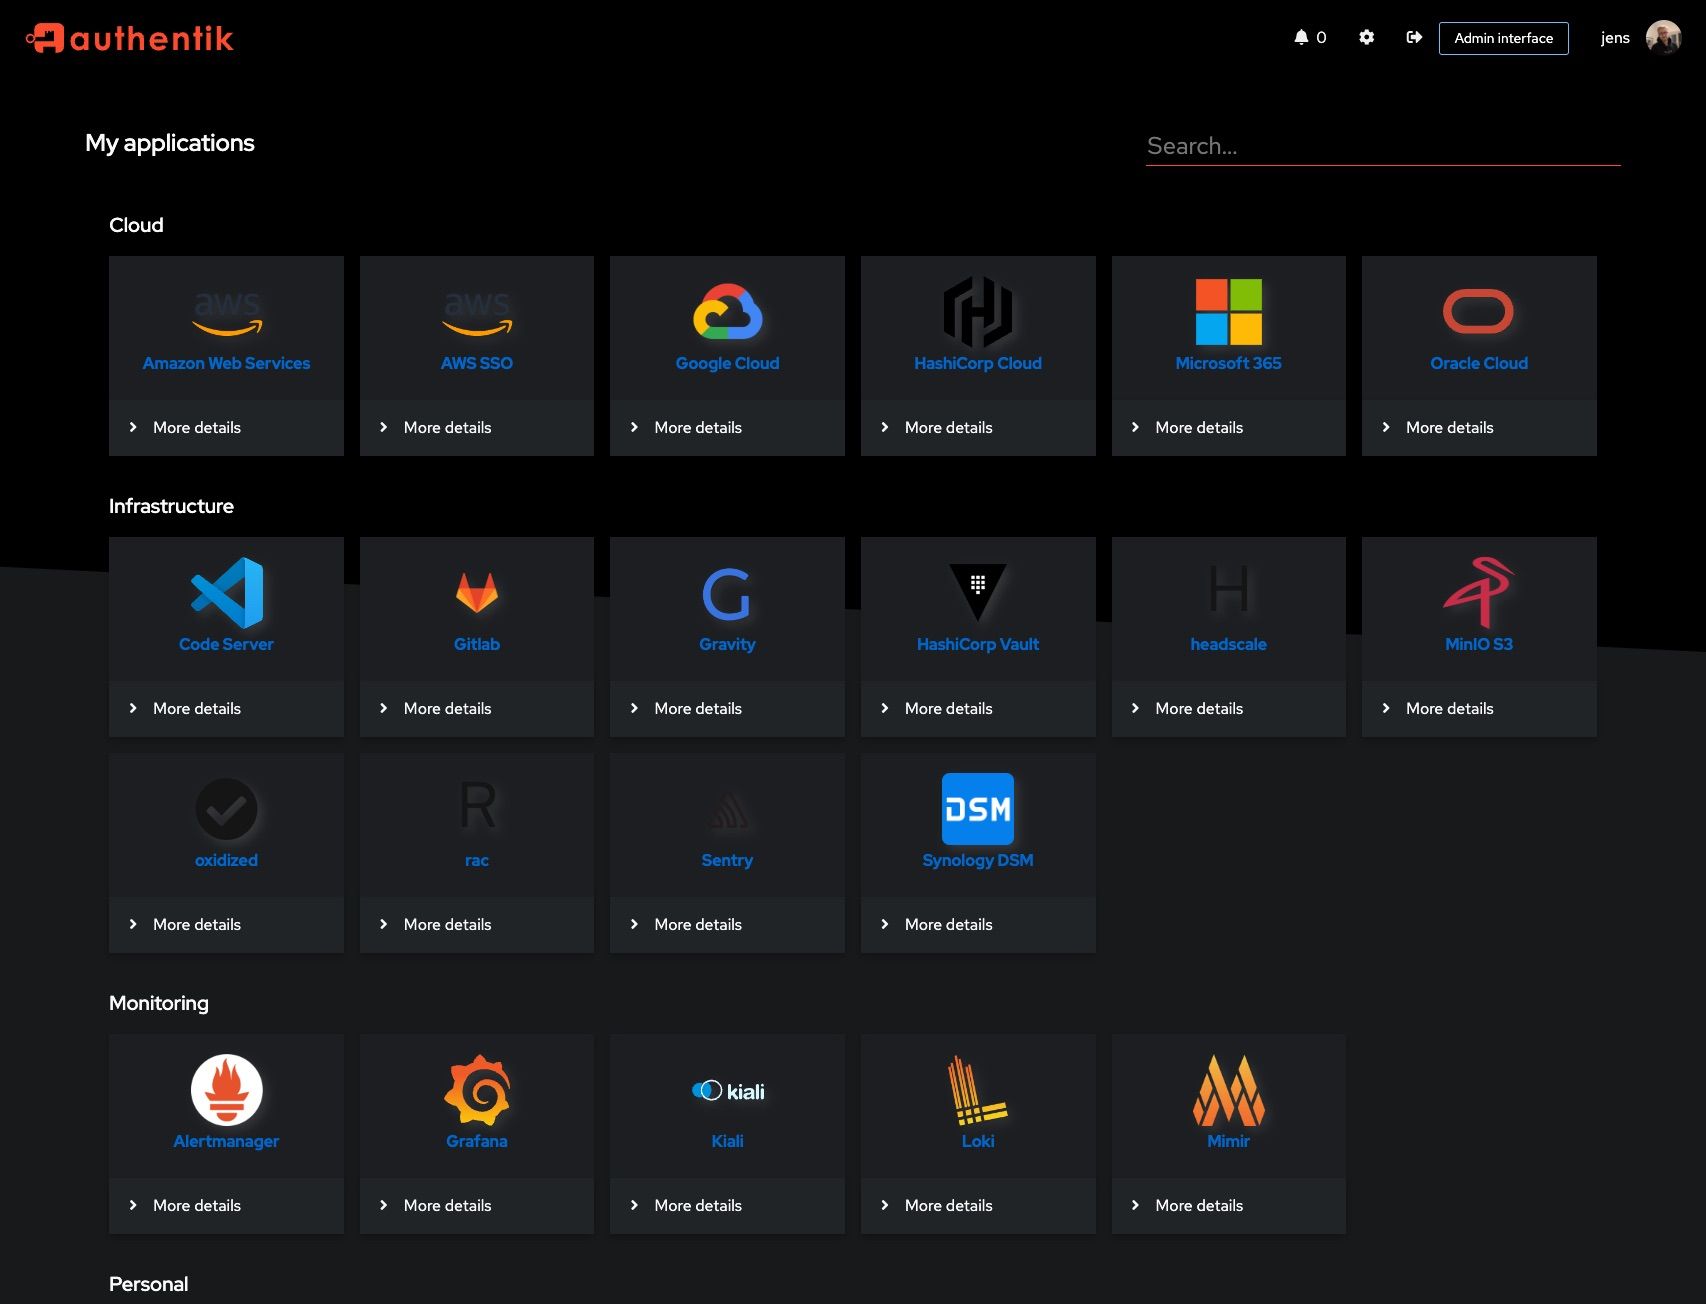
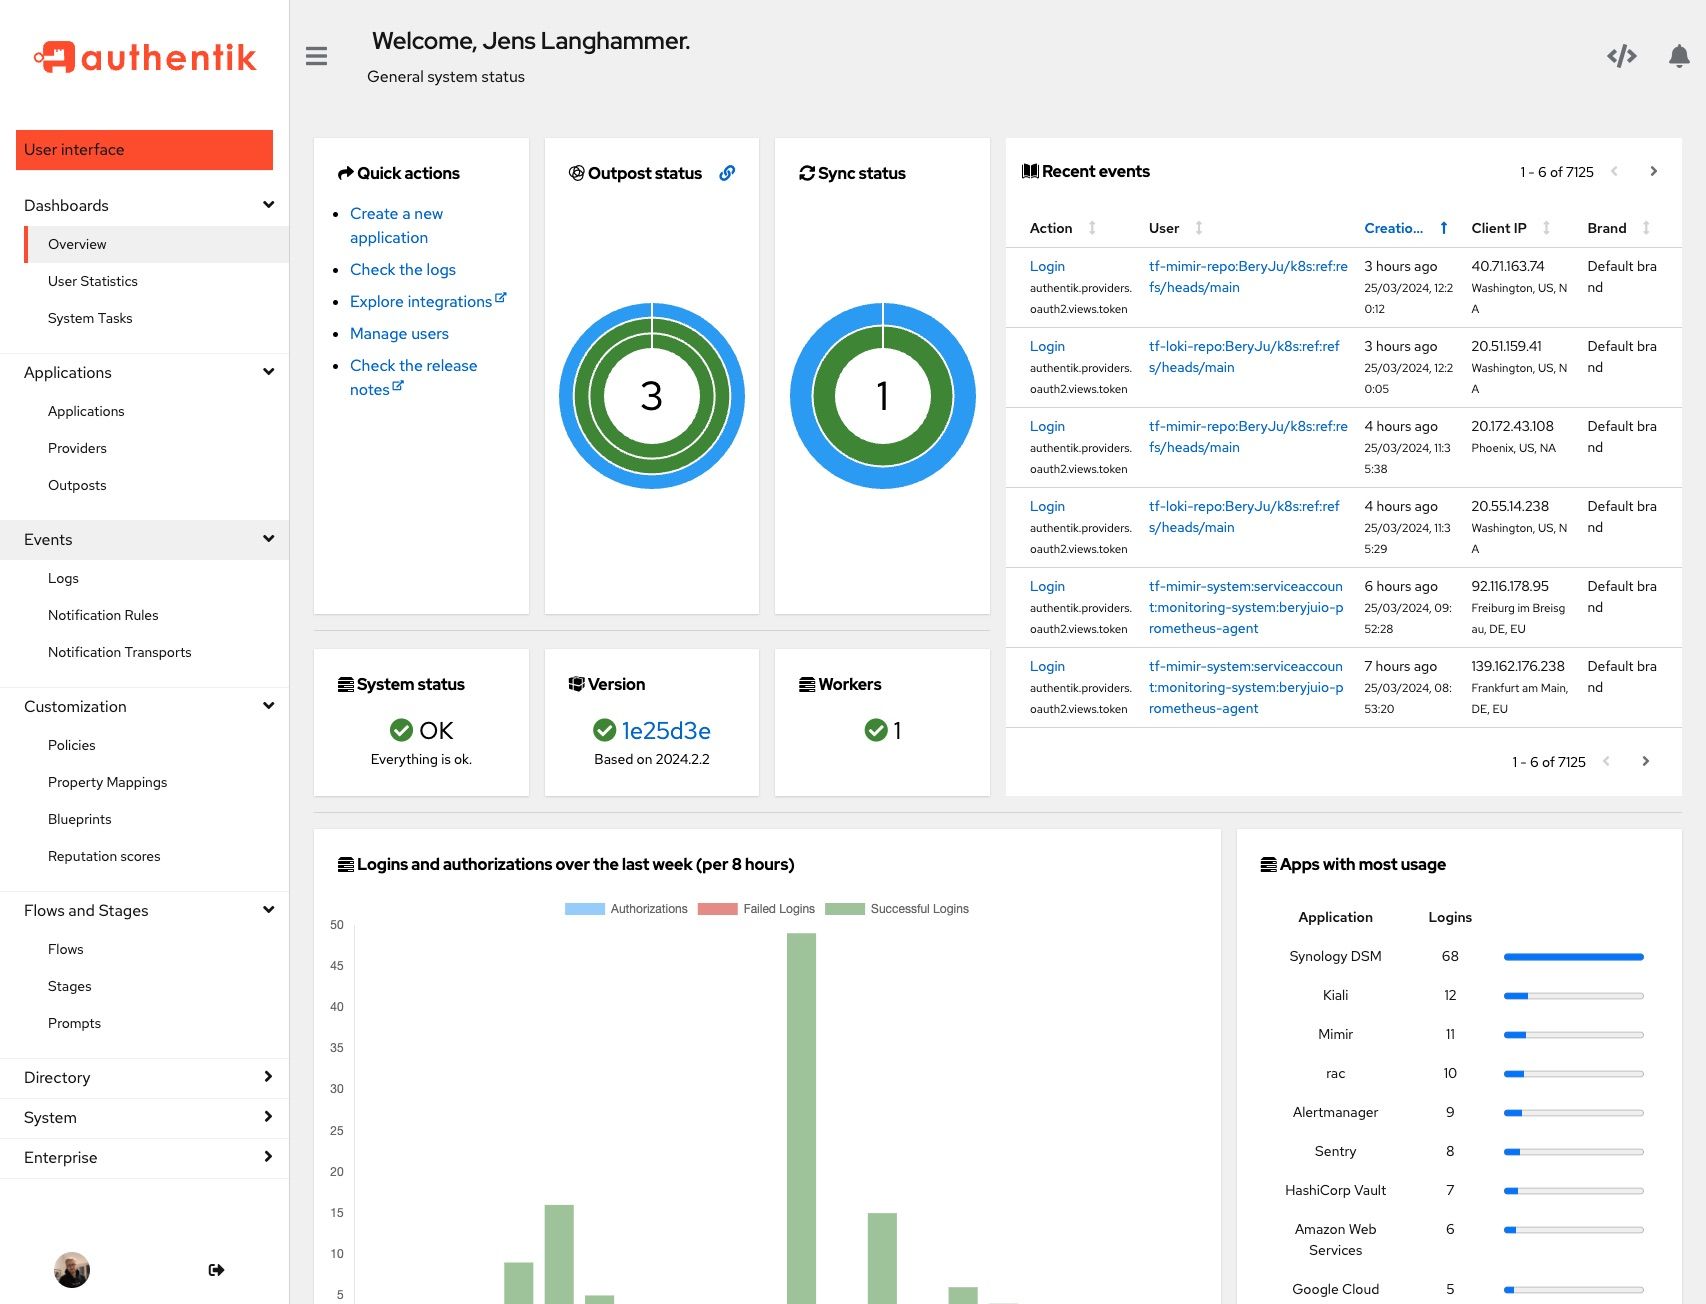
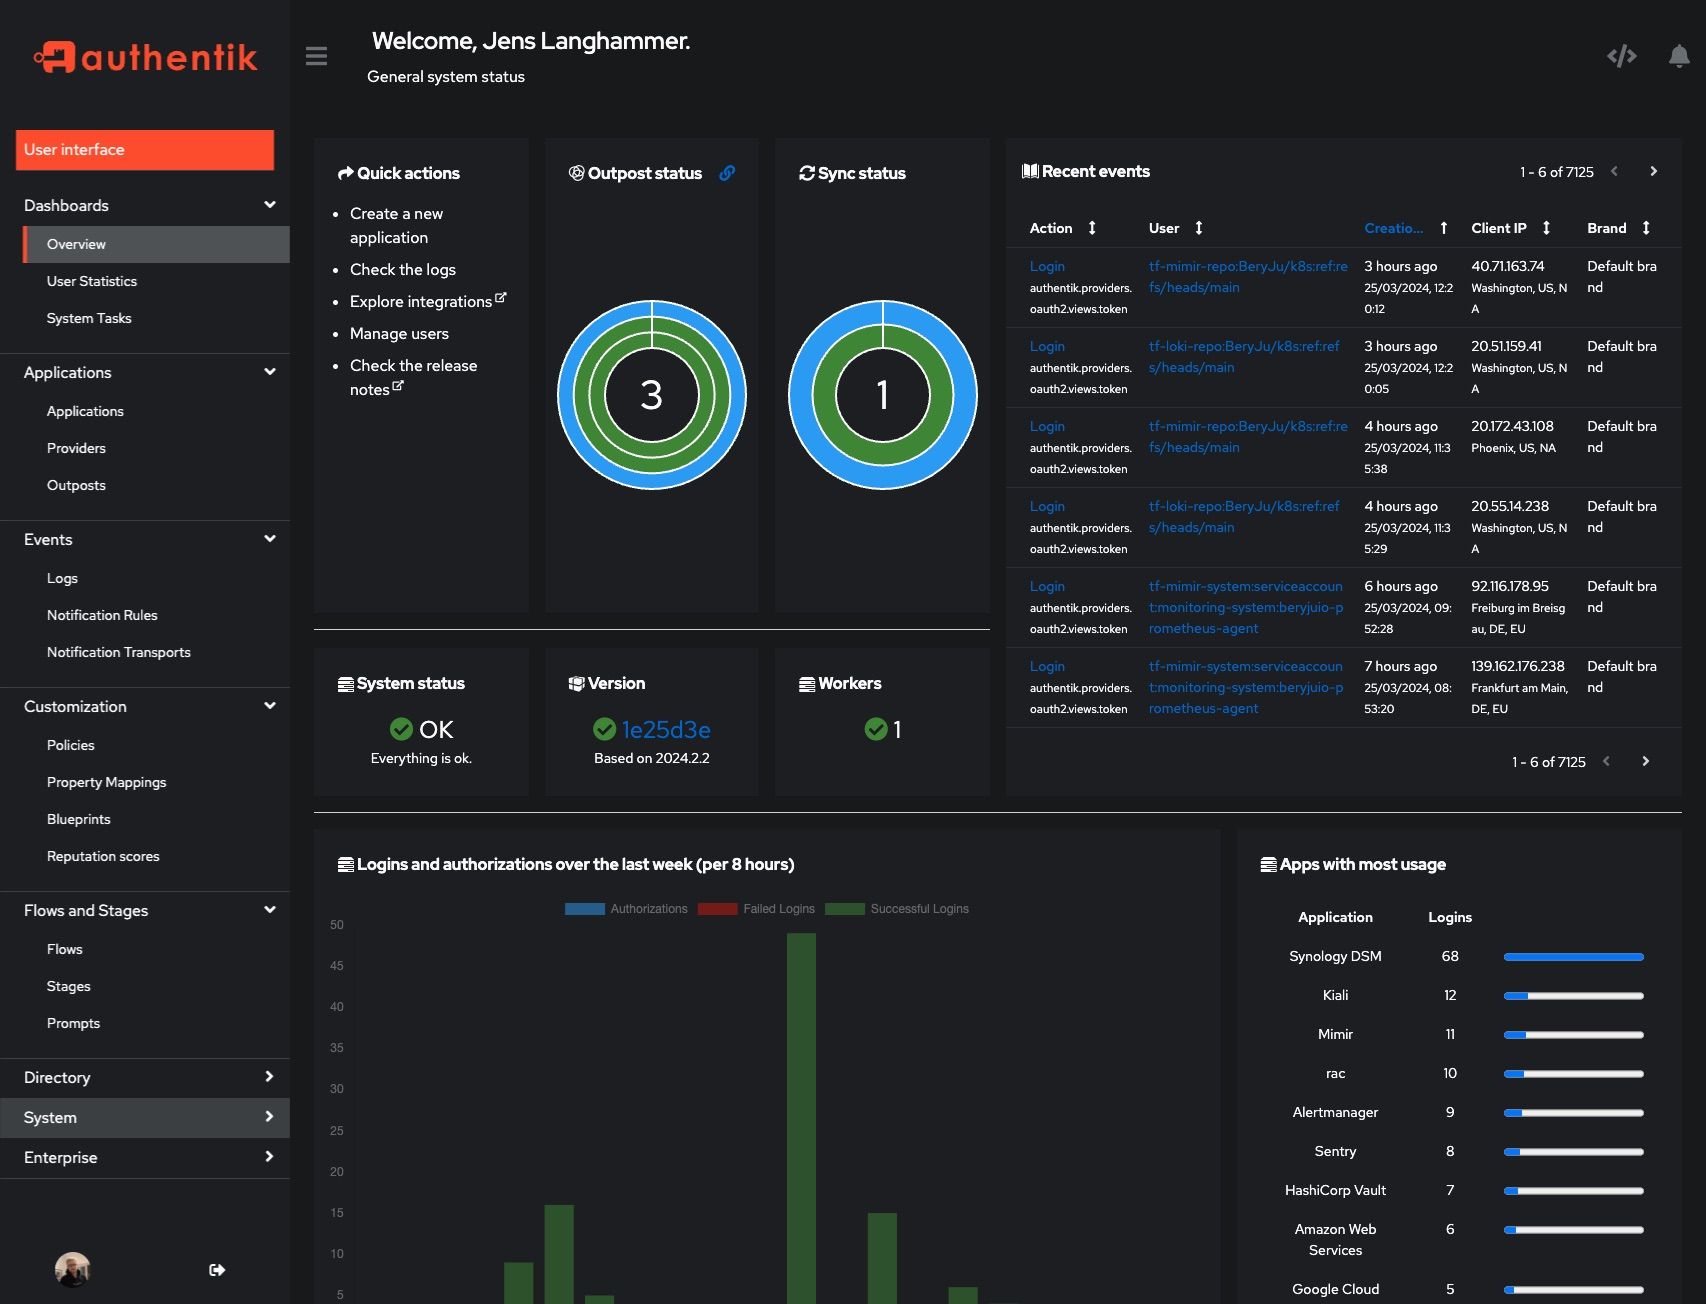
Screenshots
| Light | Dark |
|---|---|
 |  |
 |  |
Development and contributions
See the Developer Documentation for information about setting up local build environments, testing your contributions, and our contribution process.
When you contribute documentation, either to accompany a code change or as a standalone contribution, please be sure to follow our documentation Style Guide.
Security
Please see SECURITY.md.
Adoption
Using authentik? We'd love to hear your story and feature your logo. Email us at [email protected] or open a GitHub Issue/PR!
License


kubernetes
kubernetes·Go
生产级的容器编排与调度平台,用来自动化部署、扩缩容和管理跨主机的容器化应用。
容器编排+4容器 / Kubernetes
128969+8945kv1.37.22026-11-10 11:09 UTC

uptime-kuma
louislam·JavaScript
自托管的网站与服务可用性监控面板,支持 HTTP、TCP、Ping 等多种探活方式,通过实时图表和告警通知掌握服务宕机情况。
可用性监控+4容器 / Kubernetes
93444+1098.7k2.5.92026-11-10 04:49 UTC
mall
macrozheng·Java
基于 Spring Boot + MyBatis 的完整电商系统,含前台商城和后台管理,覆盖商品、订单、会员、促销等模块,用 Docker 容器化部署。
电商系统+4容器 / Kubernetes
85029+1730kv1.0.32026-09-15 02:34 UTC

moby
moby·Go
构建容器化系统的开源协作项目,提供可拼装的组件,用来搭建和定制自己的容器平台,也是 Docker 的上游基础。
容器引擎+3容器 / Kubernetes
72361+819kdocker-v29.9.32026-11-09 22:29 UTC