默认登录账号密码为 mobsf/mobsf,暴露到公网前务必修改;容器默认监听 8000 端口,需自行映射;动态分析依赖模拟器或真机环境,不是开箱即用。
Mobile-Security-Framework-MobSF
MobSFGPL-3.0活跃维护一站式移动应用安全测试框架,支持 Android、iOS 和 Windows 应用的静态与动态分析,可自动完成渗透测试、恶意软件分析和安全评估。
Mobile Security Framework (MobSF) is an automated, all-in-one mobile application (Android/iOS/Windows) pen-testing, malware analysis and security assessment framework capable of performing static and dynamic analysis.
v4.6.4发布于 2026-10-31 07:30 UTC22,186star +23 / 7 天3,810fork同步于 2026-11-10 11:23 UTC
docker pull opensecurity/mobile-security-framework-mobsf:latest
docker run -it --rm -p 8000:8000 opensecurity/mobile-security-framework-mobsf:latest 硬件要求按 README 说明
README 未说明具体硬件要求;动态分析需模拟器、仿真器、Corellium 或物理设备,非 root 安卓设备需借助 Frida Gadget。
有 Docker 镜像
一站式移动应用安全分析平台,支持 Android/iOS/Windows 静态与动态分析
一站式移动应用安全测试框架,支持 Android、iOS 和 Windows 应用的静态与动态分析,可自动完成渗透测试、恶意软件分析和安全评估。
核心能力
- 静态分析 APK、XAPK、AAB、IPA、APPX 等二进制与源码
- 动态分析支持模拟器、真机及 Frida Gadget 非 root 设备
- 通过 REST API 与 CLI 接入 DevSecOps/CI-CD 流水线
- 提供 Web API Viewer 做运行时流量与接口检查
容易踩的坑
内容由模型根据 README 生成,可能不完整或不准确,以官方文档为准。看原文 README
- v4.6.4最新正式版2026-10-31 · 2026-10-31 07:30 UTC
v4.6.4 Changelog
This release adds direct
.dexstatic analysis, replaceswkhtmltopdf/pdfkitandhttp-toolswithxhtml2pdfand a built-inmitmproxyWeb Traffic viewer, removes 9 single-use dependencies, and includes several static and dynamic analysis fixes.-
Features or Enhancements
- Added direct static analysis support for standalone Android
.dexfiles - Replaced
http-toolswithmitmproxyand added a built-in authenticated live Web Traffic viewer with dark mode and upstream proxy replay ("Send to Fuzzer") - Replaced
wkhtmltopdfandpdfkitwith pure-Pythonxhtml2pdfand confined PDF asset resolution withResourceAccessPolicy - Updated the AppSec security score calculation to use a baseline-anchored monotonic formula
- Added 26 new Android permissions to the Android permissions knowledge base
- Replaced 9 single-use dependencies (
six,distro,shelljob,colorlog,svgutils,arpy,macholib,bleach,rsa) with Python standard library or existing packages - Optimized
Dockerfilelayers and bumped OpenJDK to24.0.2and JADX to1.5.6
- Added direct static analysis support for standalone Android
-
Bug Fixes
- Fixed Android 10/11 emulator and Genymotion
frida-serverstartup crashes by staging and executingfd_serverfrom/data/local/tmp/mobsf - Fixed Android live logcat streaming by filtering on the package's effective UID(s) and keeping the Stop/Continue Streaming button responsive
- Fixed Mach-O debug symbol stripping detection by checking
N_STAB(0xe0) symbol table entries - Skipped redundant JADX per-DEX fallback decompilation when Java output is already generated
- Prevented duplicate native library (
.so) analysis ofapktool_outcopies - Fixed multi-file uploads on the home page to trigger static analysis in both synchronous and asynchronous queue modes
- Added a fallback to macOS
sipsfor iOS CgBI icon conversion whenxcrun -sdk iphoneos pngcrushis unavailable
- Fixed Android 10/11 emulator and Genymotion
What's Changed
- fix(macho): detect stripped debug symbols via N_STAB bits by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2743
- fix(appsec): use baseline-anchored monotonic security score formula by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2744
- feat(android): add direct static analysis support for DEX files by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2745
- chore(docker): optimize Dockerfile layers and bump OpenJDK 24.0.2 & JADX 1.5.6 by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2746
- fix(jadx): skip redundant per-DEX fallback when Java output is generated by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2748
- fix(home): trigger static analysis for multi-file uploads in sync and async modes by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2749
- feat(pdf): replace wkhtmltopdf and pdfkit with xhtml2pdf by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2747
- fix(ios): fallback to macOS sips when xcrun iphoneos pngcrush is unavailable by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2750
- Do not analyse apktool's copy of native libraries. by @captainrogers69 in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2752
- feat(dynamic): replace http-tools with mitmproxy and add live HTTP traffic viewer by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2753
- fix(dynamic): execute emulator frida-server from /data/local/tmp by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2754
- chore: bump version to 4.6.4, update deps, and replace 9 single-use dependencies by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2755
- chore: dark-mode Web Traffic styles, Android permissions KB, and cleanup by @ajinabraham in https://github.com/Mob
-
- v4.6.22026-10-28 · 2026-10-28 22:58 UTC
查看更新说明
v4.6.2 Changelog
This release adds dynamic analysis on physical Android devices, refreshes the web interface with a new home page and dark mode, and includes several security and performance improvements.
-
Features or Enhancements
- Added Android dynamic analysis on physical devices, with support for both rooted and stock (non-rooted) devices, plus documentation and hardened defaults for physical-device deployments
- Added a Frida Gadget APK builder to instrument apps on stock devices, including support for split APK sets
- Kept Gadget injection within Android's DEX limit and added uninstall for Gadget-injected apps
- Added a gallery of installed apps on the connected Android device, with on-demand scanning
- Added live step-by-step progress while Android dynamic analysis setup runs
- Refreshed the home page and added a dark mode toggle to the AdminLTE shell
- Added Dart string extraction from Flutter
libapp.so - Added a check that flags unauthenticated
LocalServerSocketlisteners - Added analysis of native libraries inside split APKs
- Skipped JetBrains and Flutter embedding classes during static analysis to reduce noise
- Reduced Flutter false positives in secret detection by ignoring Flutter plugin constants and tightening binary secret detection
- Cached App Link host SSRF verdicts so each host is checked and logged only once
- Sped up report loading by fetching the report DB row once instead of once per field
security.pyhardening and dependency updates- Removed the dead malwaredomainlist.com integration
- Docker images are now published from the
docker-publishenvironment; bumpeddocker/build-push-actionto 7.4.0 andactions/setup-javato 6.1.0
-
Bug Fixes
- Bounded outbound requests driven by scanned app content
- Kept APPX executable reads inside the upload directory
- Stopped the OS unzip fallback from following external symlinks
- Boolean settings are now treated as enabled only when set to
1 - Fixed Frida Gadget spawn failures by freeing port 27042 and retrying on
ProtocolError - Fixed a Docker entrypoint log-level typo so it matches
run.sh - Fixed
runserverwhen debugging
What's Changed
- fix: analyze native libraries from split APKs by @Zen1th53 in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2685
- Bump docker/build-push-action from 7.3.0 to 7.4.0 by @dependabot[bot] in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2688
- chore: remove dead malwaredomainlist.com integration by @alanhasn in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2687
- Keep APPX executable reads inside the upload directory by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2694
- Android dynamic analyzer: add physical-device foundation by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2698
- Android dynamic analyzer: support rooted physical devices by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2699
- Android dynamic analyzer: add Frida Gadget APK builder by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2700
- Android dynamic analyzer: support stock physical devices by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2701
- Document and harden Android physical-device deployments by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2702
- Android dynamic analyzer: support Gadget split APK sets by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2711
- Fix Docker entrypoint log-level typo to match run.sh by @cpuu in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2719
- Bump actions/setup-java from 6.0.1 to 6.1.0 by @dependabot[bot] in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2716
- fix: cache App Link host SSRF verdicts and
-
- v4.5.32026-09-21 · 2026-09-21 02:52 UTC
查看更新说明
v4.5.3 Changelog
-
Features or Enhancements
- Added REST API support for viewing decompiled Android XML (
type=xmlonapi/v1/view_source) for APK, Android Studio source ZIP, and AAR scans - Bumped the MobSF signature pack
- 4.5.3 dependency and supply-chain refresh: package bumps (including LIEF 0.17), GitHub Actions pinned to full commit SHAs, and related CI/release maintenance
- Replaced the third-party auto-comment Action with native
gh, and fixed repo context so welcome comments work without a checkout
- Added REST API support for viewing decompiled Android XML (
-
Bug Fixes
- Fixed DNS-rebinding SSRF by pinning HTTPTools to safe, server-side HTTP requests
- Hardened path traversal checks against Windows root-relative and drive-relative escapes
- Bounded androguard in-memory ZIP member decompression to block zip-bomb extraction
- Fixed iOS
Info.plist/CFBundleExecutablepath traversal when resolving bundled files - Fixed CSRF on dynamic analysis actions by requiring token-bearing POST (including GET-render / POST-stream for logcat)
- Rejected inactive SAML users before ACS group updates and login
- Fixed apktool not extracting PAK information correctly
- Stopped mitmdump from leaking and respawning a helper process on every dynamic analysis run
- Fixed the Maltrail malware-domain feed URL and increased the download timeout
- Fixed responsive analysis layouts (mobile nav, report summaries) and upload/request error handling, including
IntegrityErrorraces on user creation - Fixed typo
normnal→normal
What's Changed
- fix: typo normnal -> normal by @ayushmanchhabra in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2652
- fix!: apktool not extracting the pak informations properly by @AdrienHutinel in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2651
- Fix DNS rebinding SSRF with pinned safe HTTP requests. by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2670
- Replace wow-actions/auto-comment with native gh by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2672
- ci: fix Auto Comment gh repo context by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2674
- Harden path traversal against Windows root-relative escapes by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2673
- Bound androguard ZIP member decompression by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2675
- Reject inactive SAML users before ACS group updates by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2677
- Fix iOS plist-derived path traversal by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2678
- Fix CSRF in dynamic analysis actions by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2679
- Prepare 4.5.3 dependency release by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2680
- Update for /maltrail-malware-domains.txt link by @MikhailKasimov in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2662
- fix: mitmdump process leaked and respawned on every dynamic analysis run by @alanhasn in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2658
- Fix responsive layouts and request error handling by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2681
- feat: expose decompiled Android XML files via the view_source REST API by @alanhasn in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2659
- bump signatures by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2682
- docs: note CSRF POST and DOM XSS rules in AGENTS.md by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2684
New Contributors
- @MikhailKasimov made their first contribution in https://github.com/MobSF/Mobile-Security-Framework
-
- v4.5.22026-08-10 · 2026-08-10 06:20 UTC
查看更新说明
v4.5.2 Changelog
-
Features or Enhancements
- Updated Android certificate analysis with apksigner from build-tools 37.0.0 and apktool 3.x support for more robust, version-agnostic cert parsing
- Added high-confidence known secret format detection in Android/iOS string analysis (GitHub, Slack, Stripe, OpenAI, PEM keys, and more)
- Migrated VirusTotal integration to API v3 with large-file upload support (up to 650MB)
- CI/Docker supply-chain hardening: SBOM attestations, Actions updates, Postgres 18 compose layout, and PyPI publishing via OIDC Trusted Publishing
-
Bug Fixes
- Fixed CSRF "null origin" error during SAML SSO login (e.g. Keycloak)
- Fixed formatting in
SKIP_CLASS_PATHlist - Fixed Android rule to match the literal mode argument in
getSharedPreferences
What's Changed
- Update: certificate analysis (apksigner) by @AdrienHutinel in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2630
- fix csrf error by @Antiksec in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2633
- Fix formatting in SKIP_CLASS_PATH list by @Zen1th53 in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2634
- fix(rules): match the literal mode argument in getSharedPreferences by @Eljees in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2638
- ci: bump docker workflow actions and add SBOM attestations by @kobihikri in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2639
- Detect known secret formats in Android/iOS string analysis by @mmmugh in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2640
- ci/docker: supply-chain Actions updates and Postgres 18 compose layout by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2643
- Migrate VirusTotal integration to API v3 by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2644
- chore: bump Python dependencies by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2645
- ci: publish to PyPI with OIDC Trusted Publishing by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2646
New Contributors
- @AdrienHutinel made their first contribution in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2630
- @Zen1th53 made their first contribution in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2634
- @Eljees made their first contribution in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2638
- @kobihikri made their first contribution in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2639
- @mmmugh made their first contribution in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2640
Full Changelog: https://github.com/MobSF/Mobile-Security-Framework-MobSF/compare/v4.5.1...v4.5.2
-
- v4.5.12026-07-06 · 2026-07-06 00:04 UTC
查看更新说明
v4.5.1 Changelog
- Features or Enhancements
- Added Jailbroken iOS Device support in MobSF, Tested in iPhone 6s and 8 with Checkra1n and Palera1n jailbreaks [Early Beta]. See docs: https://mobsf.github.io/docs/#/dynamic_analyzer_docker?id=jailbroken-ios-device-beta
- Added a new android rule to flag Webview mixed content
- Bug Fixes
- Macho Debug Symbol False positive fix in objdump
- Security
- Fixed Multiple Security issues
- https://github.com/MobSF/Mobile-Security-Framework-MobSF/security/advisories/GHSA-95px-34x5-p37h
- https://github.com/MobSF/Mobile-Security-Framework-MobSF/security/advisories/GHSA-x768-8642-mmq9
- https://github.com/MobSF/Mobile-Security-Framework-MobSF/security/advisories/GHSA-3p54-567p-2wpr
- https://github.com/MobSF/Mobile-Security-Framework-MobSF/security/advisories/GHSA-8j49-mmcx-4mp5
- Fixed Multiple Security issues
What's Changed
- Jailbroken iOS Device Support by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2536
- [HOTFIX] Fix false positive in debug symbol stripping check using objdump by @yushawnwong in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2616
- Add Android WebView mixed-content detection rule by @potato-20 in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2618
- [HOTFIX][Security] Security Updates July 5 2026 by @ajinabraham in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2627
New Contributors
- @yushawnwong made their first contribution in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2616
- @potato-20 made their first contribution in https://github.com/MobSF/Mobile-Security-Framework-MobSF/pull/2618
Full Changelog: https://github.com/MobSF/Mobile-Security-Framework-MobSF/compare/v4.4.6...v4.5.1
- Features or Enhancements
用户点评
登录用户的真实使用记录,可按版本和硬件筛选共 0 条
还没有人点评。第一个说出真实体验的人最有价值。
Mobile Security Framework (MobSF)

Mobile Security Framework (MobSF) is a security research platform for mobile applications in Android, iOS, and Windows Mobile. MobSF can be used for a variety of use cases such as mobile application security, penetration testing, malware analysis, and privacy analysis. The Static Analyzer supports popular mobile app binaries and libraries (APK, XAPK, AAB, JAR, AAR, DEX, SO, IPA, DYLIB, A, APPX) as well as Android and iOS source code. Meanwhile, the Dynamic Analyzer supports both Android and iOS applications across emulators, simulators, Corellium, and physical devices (including stock non-rooted Android devices via Frida Gadget), offering an interactive platform for instrumented testing, runtime data inspection, and live web traffic analysis. MobSF seamlessly integrates with your DevSecOps or CI/CD pipeline via REST APIs and CLI tools.
Made with  in India




MobSF is also bundled with BlackArch and Pentoo.
Support MobSF

Has MobSF made a difference for you? Show your support and help us innovate with a donation. It's easy to build open source, maintaining one is a different story.
Long live open source!
Documentation
Quick setup with docker
docker pull opensecurity/mobile-security-framework-mobsf:latest
docker run -it --rm -p 8000:8000 opensecurity/mobile-security-framework-mobsf:latest

# Default username and password: mobsf/mobsf

- Try MobSF Static Analyzer Online: mobsf.live
- MobSF in CI/CD: mobsfscan
- Conference Presentations: Slides & Videos
- MobSF Online Course: OpSecX MAS
- What's New: See Changelog
Author

e-Learning Courses & Certifications
 Automated Mobile Application Security Assessment with MobSF - MAS
 Android Security Tools Expert - ATX
MobSF Support
- Free Support: Free limited support, questions, help and discussions, join our Slack channel
- Enterprise Support: Priority feature requests, live support & onsite training, see

Contribution, Feature Requests & Bugs
- Read CONTRIBUTING.md before opening bugs, feature requests and pull request.
- For Project updates and announcements, follow @ajinabraham or @OpenSecurity_IN.
- Github Issues are only for tracking bugs and feature requests. Do not post support or help queries there. We have a slack channel for that.
Static Analysis - Android
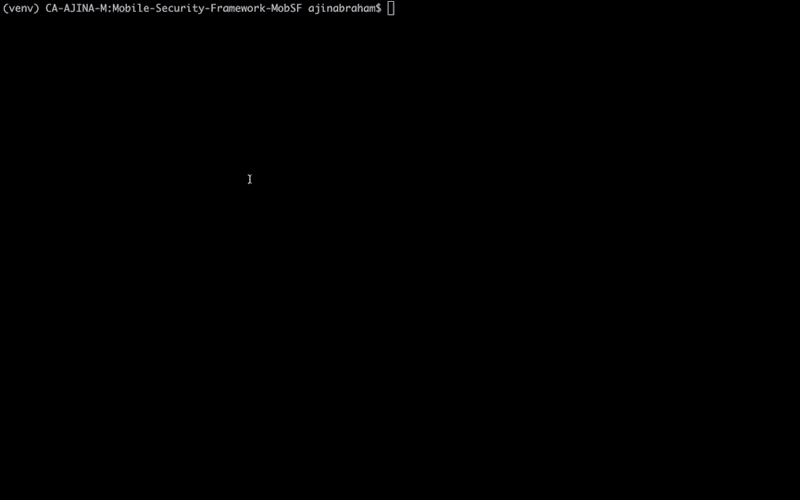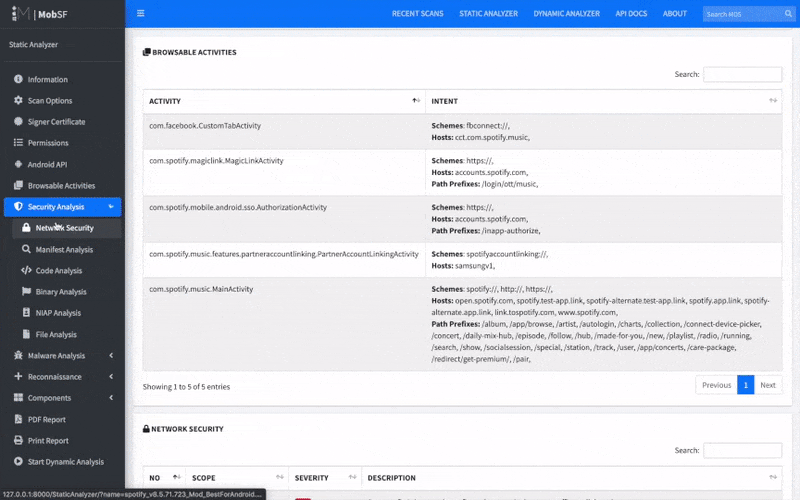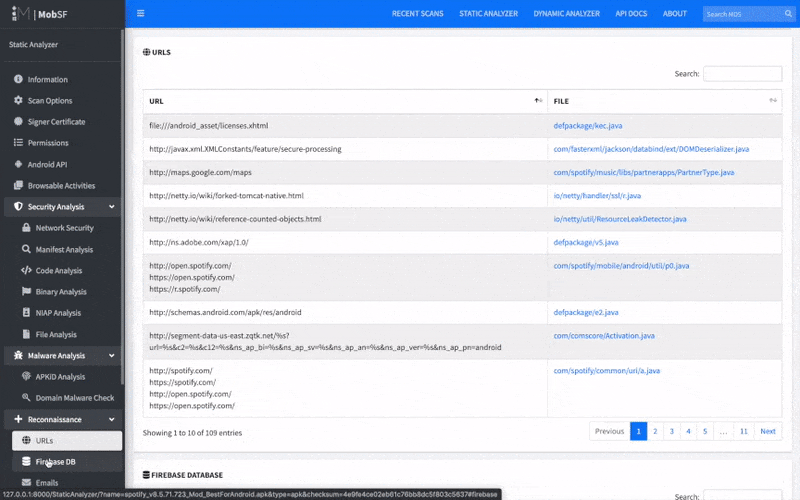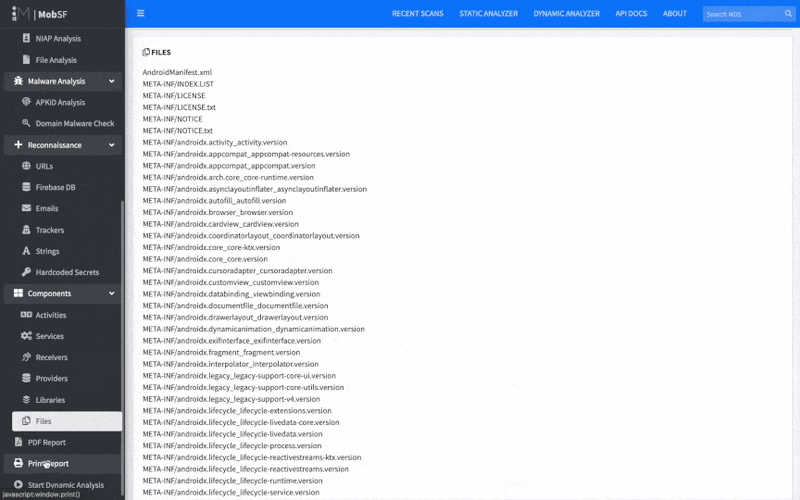
Static Analysis - iOS

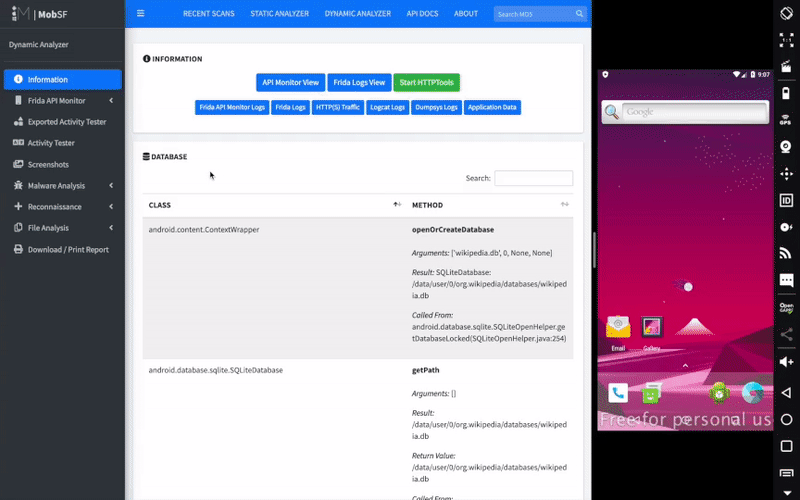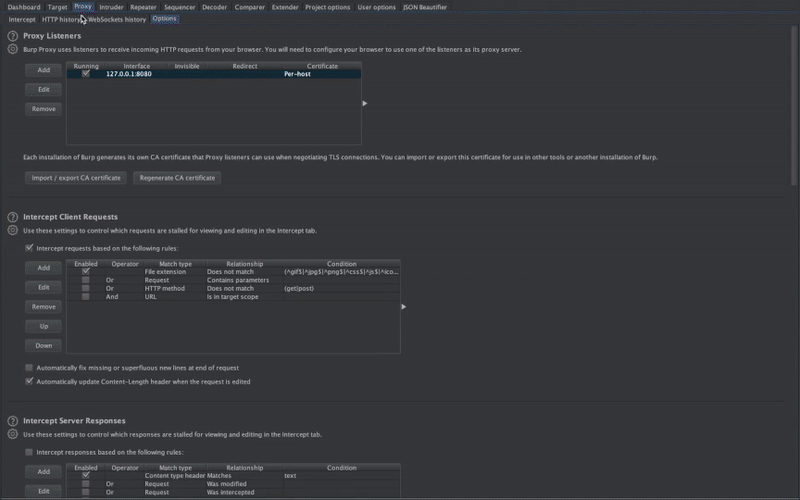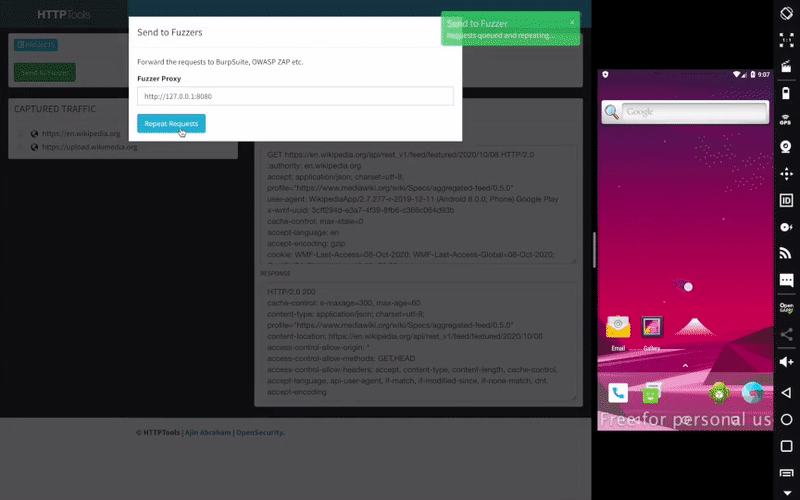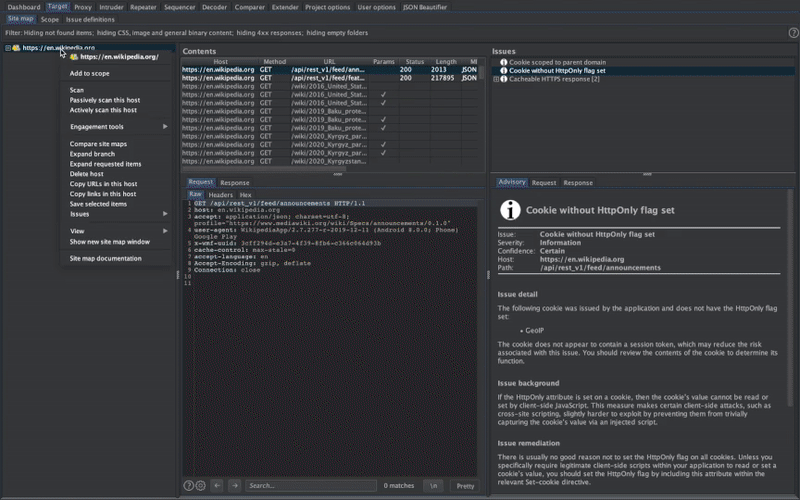
Dynamic Analysis - Android APK

Web API Viewer
Dynamic Analysis - iOS IPA
Past Collaborators


Honorable Contributors & Shoutouts
- Amrutha VC - For the new MobSF logo
- Dominik Schlecht - For the awesome work on adding Windows Phone App Static Analysis to MobSF
- Esteban - Better Android Manifest Analysis and Static Analysis Improvement.
- Matan Dobrushin - For adding Android ARM Emulator support to MobSF - Special thanks goes for cuckoo-droid
- Shuxin - Android Binary Analysis
- Abhinav Saxena - (@xandfury) - For Travis CI and Logging integration
 Netguru (@karolpiateknet, @mtbrzeski) - For iOS Swift support, Rule contributions and SAST refactoring.
- Maxime Fawe - (@Arenash13) - For Matching Strategy implementation of SAST pattern matching algorithms.
- Abhinav Sejpal (@Abhinav_Sejpal) - For poking me with bugs, feature requests, and UI & UX suggestions
- Anant Srivastava (@anantshri) - For Activity Tester Idea
- Anto Joseph (@antojoseph) - For the help with SuperSU
- Bharadwaj Machiraju (@tunnelshade) - For writing pyWebProxy from scratch
- Rahul (@c0dist) - Kali Support
- MindMac - For writing Android Blue Pill
- Oscar Alfonso Diaz - (@OscarAkaElvis) - For Dockerfile contributions
- Thomas Abraham - For JS Hacks on UI
- Tim Brown (@timb_machine) - For the iOS Binary Analysis Ruleset
- Shanil Prasad (@Rajuraju14) - For improving iOS ATS Analysis
- Jovan Petrovic (@JovanPetrovic) - For sponsoring a server to host mobsf.live
open-webui
open-webui·Svelte
自托管的大模型对话界面,兼容 Ollama、OpenAI API 等后端,内置 RAG 与 MCP 支持,让团队快速搭建私有 AI 聊天入口。
大模型界面+4API 开发与调试
158285+31323kv0.13.32026-11-10 08:23 UTC
hoppscotch
hoppscotch·TypeScript
轻量级开源 API 开发调试工具,支持 REST、GraphQL、WebSocket 等协议,提供 Web、桌面和 CLI 多端使用,可离线部署,是 Postman 和 Insomnia 的开源替代品。
API 调试+4API 开发与调试
80770+76.2k2026.10.12026-11-05 08:16 UTC

bruno
usebruno·JavaScript
轻量级开源 API 调试 IDE,支持 REST、GraphQL 和 OpenAPI,用 Git 管理接口集合,可替代 Postman/Insomnia。
API 调试+4API 开发与调试
48317+603.1kv4.3.02026-11-09 17:13 UTC
full-stack-fastapi-template
fastapi·TypeScript
用 FastAPI + React + PostgreSQL 搭好的全栈项目脚手架,自带 JWT 登录、Docker Compose 和 CI 配置,省去从零搭建后端接口、前端页面和部署流程的麻烦。
全栈模板+4API 开发与调试
46218+359.2k0.12.02026-11-03 13:46 UTC