扫描本地 containers-storage 镜像必须显式加 --from containers-storage,普通镜像引用不会去那里查找;rootless 存储需在 podman unshare 内执行;从源码构建需加 -tags containers_image_openpgp,exclude_graphdriver_btrfs

curl -sSfL https://get.anchore.io/grype | sudo sh -s -- -b /usr/local/bin 硬件要求按 README 说明
README 未说明硬件要求,未提及显存或 GPU 需求
扫描容器镜像、文件系统和 SBOM 中已知漏洞的命令行工具,适合在 CI 或本地快速排查依赖风险
扫描容器镜像和文件系统中的软件包,找出已知漏洞并输出 SBOM 与漏洞报告,适合接入 CI 做供应链安全把关。
核心能力
- 扫描容器镜像、文件系统与 SBOM 三类目标
- 覆盖 Alpine、Debian、Ubuntu、RHEL 等主流 OS 包生态
- 支持 Ruby、Java、Python、Go、Rust 等语言包
- 用 EPSS、KEV 与风险评分做威胁优先级排序
- 支持 OpenVEX 过滤和补充扫描结果
容易踩的坑
内容由模型根据 README 生成,可能不完整或不准确,以官方文档为准。看原文 README
- v0.121.3最新正式版2026-11-09 · 2026-11-09 15:17 UTC
Additional Changes
- further CPE to more precise package identifier mappings [PR #3886 @westonsteimel]
Dependencies
18 dependency changes (8 updated, 10 removed). 8 vulnerabilities remediated.
🟢 Remediated (8)
- GHSA-pxq6-2prw-chj9 (Medium) — github.com/docker/docker
- GHSA-rg2x-37c3-w2rh (High) — github.com/docker/docker
- GHSA-vp62-88p7-qqf5 (Medium) — github.com/docker/docker
- GHSA-x86f-5xw2-fm2r (High) — github.com/docker/docker
- GO-2026-4887 (High) — github.com/docker/docker
- GO-2026-6860 (High) — golang.org/x/net
- GO-2026-6866 (Medium) — golang.org/x/net
- GO-2026-6888 (Critical) — github.com/andybalholm/brotli
- github.com/anchore/syft
v1.57.0→v1.57.1 - github.com/andybalholm/brotli
v1.2.0→v1.2.8(🟢 remediated GO-2026-6888) - github.com/bmatcuk/doublestar/v4
v4.10.3→v4.10.4 - github.com/gkampitakis/go-snaps
v0.5.24→v0.5.25 - github.com/gpustack/gguf-parser-go
v0.27.0→v0.28.1 - github.com/moby/sys/mountinfo
v0.7.2→v0.7.3 - go.yaml.in/yaml/v3
v3.0.5→v3.0.6 - golang.org/x/net
v0.61.0→v0.62.0(🟢 remediated GO-2026-6860, GO-2026-6866)
- github.com/cenkalti/backoff/v5
v5.0.3 - github.com/docker/docker
v28.5.2+incompatible(🟢 remediated GHSA-pxq6-2prw-chj9, GHSA-rg2x-37c3-w2rh, GHSA-vp62-88p7-qqf5, GHSA-x86f-5xw2-fm2r, GO-2026-4887) - github.com/grpc-ecosystem/grpc-gateway/v2
v2.30.0 - github.com/moby/sys/atomicwriter
v0.1.0 - github.com/moby/sys/sequential
v0.6.0 - github.com/moby/term
v0.5.2 - github.com/morikuni/aec
v1.1.0 - go.opentelemetry.io/otel/exporters/otlp/otlptrace
v1.46.0 - go.opentelemetry.io/otel/exporters/otlp/otlptrace/otlptracehttp
v1.46.0 - go.opentelemetry.io/proto/otlp
v1.11.0
- v0.121.22026-11-05 · 2026-11-05 21:22 UTC
查看更新说明
Bug Fixes
- deterministic ordering of db search match results [PR #3883 @wagoodman]
Dependencies
2 dependency changes (2 updated).
- github.com/anchore/stereoscope
v0.4.0→v0.4.1 - github.com/anchore/syft
v1.56.0→v1.57.0
- v0.121.12026-11-02 · 2026-11-02 17:29 UTC
查看更新说明
Bug Fixes
- extract the quality gate debug artifact outside the checkout [PR #3875 @wagoodman]
- incorrect constraint for versionless purls in openvex [PR #3874 @kzantow]
- report additional version-range records for a package [PR #3782 @jspilman]
- report a package's vulnerability as added or removed only when its affected record set changes [PR #3784 @jspilman]
- report the lowest overlapping AlmaLinux fix [PR #3783 @jspilman]
- report fix date and kind changes under the package [PR #3781 @jspilman]
- label db diff databases in the order they were provided [PR #3816 @bot190]
- time out stalled db diff downloads [PR #3858 @wagoodman]
- only remove db diff directories that grype created [PR #3828 @wagoodman]
- make db diff --packages and --vulns include only what was requested [PR #3815 @bot190]
Performance
- index ignore rules by vulnerability ID [PR #3817 @juanjsebgarcia]
- speed up db diff and reduce its memory and temp disk use [PR #3813 @bot190]
Additional Changes
- grype 0.119.0 allocates without bound on a CycloneDX machine-learning-model component with no purl and no CPE [Issue #3767]
- add a directory for grype-specific match labels [PR #3849 @wagoodman]
- let go-make own the go version and move images to debian13 [PR #3840 @wagoodman]
Dependencies
41 dependency changes (39 updated, 1 added, 1 removed). 1 vulnerability remediated.
🟢 Remediated (1)
- GHSA-mgcc-cww5-fp2q (High) — github.com/go-jose/go-jose/v4
- github.com/Microsoft/go-winio
v0.6.3-0.ad3df93→v0.6.3-0.f19d971 - github.com/ProtonMail/go-crypto
v1.4.1→v1.5.2 - github.com/anchore/clio
v0.1.1→v0.1.2 - github.com/anchore/stereoscope
v0.3.4→v0.4.0 - github.com/anchore/syft
v1.55.0→v1.56.0 - github.com/bmatcuk/doublestar/v4
v4.10.2→v4.10.3 - github.com/containerd/containerd/v2
v2.4.1→v2.4.2 - github.com/containerd/stargz-snapshotter/estargz
v0.18.2→v0.19.0 - github.com/deitch/magic
v0.0.0-c67ab88→v1.0.0 - github.com/docker/cli
v29.8.2+incompatible→v29.9.2+incompatible - github.com/docker/docker-credential-helpers
v0.9.8→v0.9.10 - github.com/docker/go-connections
v0.8.1→v0.8.2 - github.com/gabriel-vasile/mimetype
v1.4.15→v1.4.16 - github.com/github/go-spdx/v2
v2.7.1→v2.8.0 - github.com/gkampitakis/go-snaps
v0.5.23→v0.5.24 - github.com/go-jose/go-jose/v4
v4.1.5→v4.1.6(🟢 remediated GHSA-mgcc-cww5-fp2q) - github.com/go-test/deep
v1.1.1→v1.1.2 - github.com/google/pprof
v0.0.0-ef3492d→v0.0.0-1facf8f - github.com/gookit/color
v1.6.2→v1.6.3 - github.com/gpustack/gguf-parser-go
v0.26.4→v0.27.0 - github.com/klauspost/compress
v1.20.1→v1.20.3 - github.com/klauspost/pgzip
v1.2.6→v1.2.7 - github.com/mattn/go-runewidth
v0.0.27→v0.0.31 - github.com/mattn/go-sqlite3
v1.14.48→v1.14.52 - github.com/moby/moby/api
v1.56.0→v1.56.1 - github.com/moby/moby/client
v0.6.0→v0.6.2 - github.com/ncruces/go-strftime
v1.0.0→v1.1.0 - github.com/sigstore/fulcio
v1.8.7→v1.8.8 - github.com/vbauerster/cupwriter
v0.0.4→v0.0.5 - github.com/vbauerster/mpb/v8 `v
- v0.121.02026-10-19 · 2026-10-19 20:32 UTC
查看更新说明
Added Features
- OS End of life warnings should account for SupportEnd date from the distro release information [Issue #3230] [PR #3787 @tomersein]
- Licensing: copyright owner missing, needed for Debian packaging [Issue #3501] [PR #3791 @wagoodman]
Bug Fixes
- fix(db-build) allow configuring sqlite cache size at db build time [PR #3814 @willmurphyscode]
- Carry AlmaLinux fix dates onto replaced RHEL matches [PR #3773 @wagoodman]
- carry fix availability through extended support fix merging [PR #3809 @bot190]
- upgrade to golang.org/x/net v0.61.0 [PR #3802 @westonsteimel]
- Swift Package Manager packages miss GitHub Swift advisories (searched by identity, not repository path) [Issue #3795] [PR #3713 @az-catch]
Additional Changes
- bump go-make module and action together [PR #3793 @wagoodman]
Dependencies
50 dependency changes (47 updated, 1 added, 2 removed). 5 vulnerabilities remediated.
🟢 Remediated (5)
- GO-2026-6603 (High) — golang.org/x/net
- GO-2026-6610 (High) — golang.org/x/net
- GO-2026-6611 (High) — golang.org/x/net
- GO-2026-6612 (Critical) — golang.org/x/net
- GO-2026-6617 (High) — golang.org/x/net
- cloud.google.com/go/auth
v0.23.2→v0.23.3 - cloud.google.com/go/compute/metadata
v0.9.0→v0.9.1 - cloud.google.com/go/storage
v1.65.1→v1.68.0 - github.com/GoogleCloudPlatform/opentelemetry-operations-go/detectors/gcp
v1.33.0→v1.34.0 - github.com/anchore/syft
v1.54.1→v1.55.0 - github.com/aws/aws-sdk-go-v2
v1.44.0→v1.47.1 - github.com/aws/aws-sdk-go-v2/config
v1.32.40→v1.33.6 - github.com/aws/aws-sdk-go-v2/credentials
v1.19.39→v1.20.6 - github.com/aws/aws-sdk-go-v2/feature/ec2/imds
v1.18.40→v1.20.1 - github.com/aws/aws-sdk-go-v2/internal/configsources
v1.4.40→v1.5.4 - github.com/aws/aws-sdk-go-v2/internal/endpoints/v2
v2.7.40→v2.8.4 - github.com/aws/aws-sdk-go-v2/internal/v4a
v1.4.41→v1.5.4 - github.com/aws/aws-sdk-go-v2/service/internal/checksum
v1.10.0→v1.11.5 - github.com/aws/aws-sdk-go-v2/service/internal/presigned-url
v1.13.40→v1.14.4 - github.com/aws/aws-sdk-go-v2/service/internal/s3shared
v1.19.41→v1.20.4 - github.com/aws/aws-sdk-go-v2/service/s3
v1.108.0→v1.114.0 - github.com/aws/aws-sdk-go-v2/service/signin
v1.6.0→v1.10.1 - github.com/aws/aws-sdk-go-v2/service/sso
v1.34.0→v1.38.1 - github.com/aws/aws-sdk-go-v2/service/ssooidc
v1.39.0→v1.43.1 - github.com/aws/aws-sdk-go-v2/service/sts
v1.46.0→v1.51.1 - github.com/github/go-spdx/v2
v2.7.0→v2.7.1 - github.com/go-git/go-billy/v5
v5.9.1→v5.9.2 - github.com/go-git/go-git/v5
v5.19.2→v5.19.3 - github.com/google/s2a-go
v0.1.9→v0.1.10 - github.com/googleapis/enterprise-certificate-proxy
v0.3.20→v0.3.22 - github.com/googleapis/gax-go/v2
v2.24.0→v2.24.1 - github.com/gookit/color
v1.6.1→v1.6.2 - github.com/gpustack/gguf-parser-go
v0.26.3→v0.26.4 - github.com/hashicorp/go-getter
v1.8.9→v1.8.10 - github.com/pb33f/ordered-map/v2
v2.3.1→v2.3.2 - github.com/pjbgf/sha1cd
v0.6.0→v0.7.0 - github.com/spiffe/go-spiffe/v2
v2.7.0→v2.8.1 - golang.org/x/crypto
v0.57.0→v0.58.0 - golang.org/x/net
v0.59.0→v0.61.0**(🟢 remediated GO-2026-6603, [
- v0.120.12026-10-06 · 2026-10-06 20:46 UTC
查看更新说明
Bug Fixes
- run unit tests on windows and fix the handle leaks it surfaced [PR #3766 @wagoodman]
- Table presenter appends a spurious ", ..." to the FIX column when all fix versions are already shown [Issue #3760] [PR #3770 @arpitjain099]
Dependencies
9 dependency changes (9 updated).
- github.com/anchore/go-rpmdb
v0.2.1→v0.2.2 - github.com/anchore/stereoscope
v0.3.3→v0.3.4 - github.com/anchore/syft
v1.54.0→v1.54.1 - github.com/docker/cli
v29.8.1+incompatible→v29.8.2+incompatible - github.com/klauspost/compress
v1.20.0→v1.20.1 - github.com/secure-systems-lab/go-securesystemslib
v0.11.0→v0.11.1 - github.com/sigstore/protobuf-specs
v0.5.1→v0.5.2 - github.com/sigstore/sigstore
v1.10.8→v1.10.11 - github.com/sylabs/sif/v2
v2.24.1→v2.24.2
用户点评
登录用户的真实使用记录,可按版本和硬件筛选共 0 条
还没有人点评。第一个说出真实体验的人最有价值。
Grype
A vulnerability scanner for container images and filesystems.
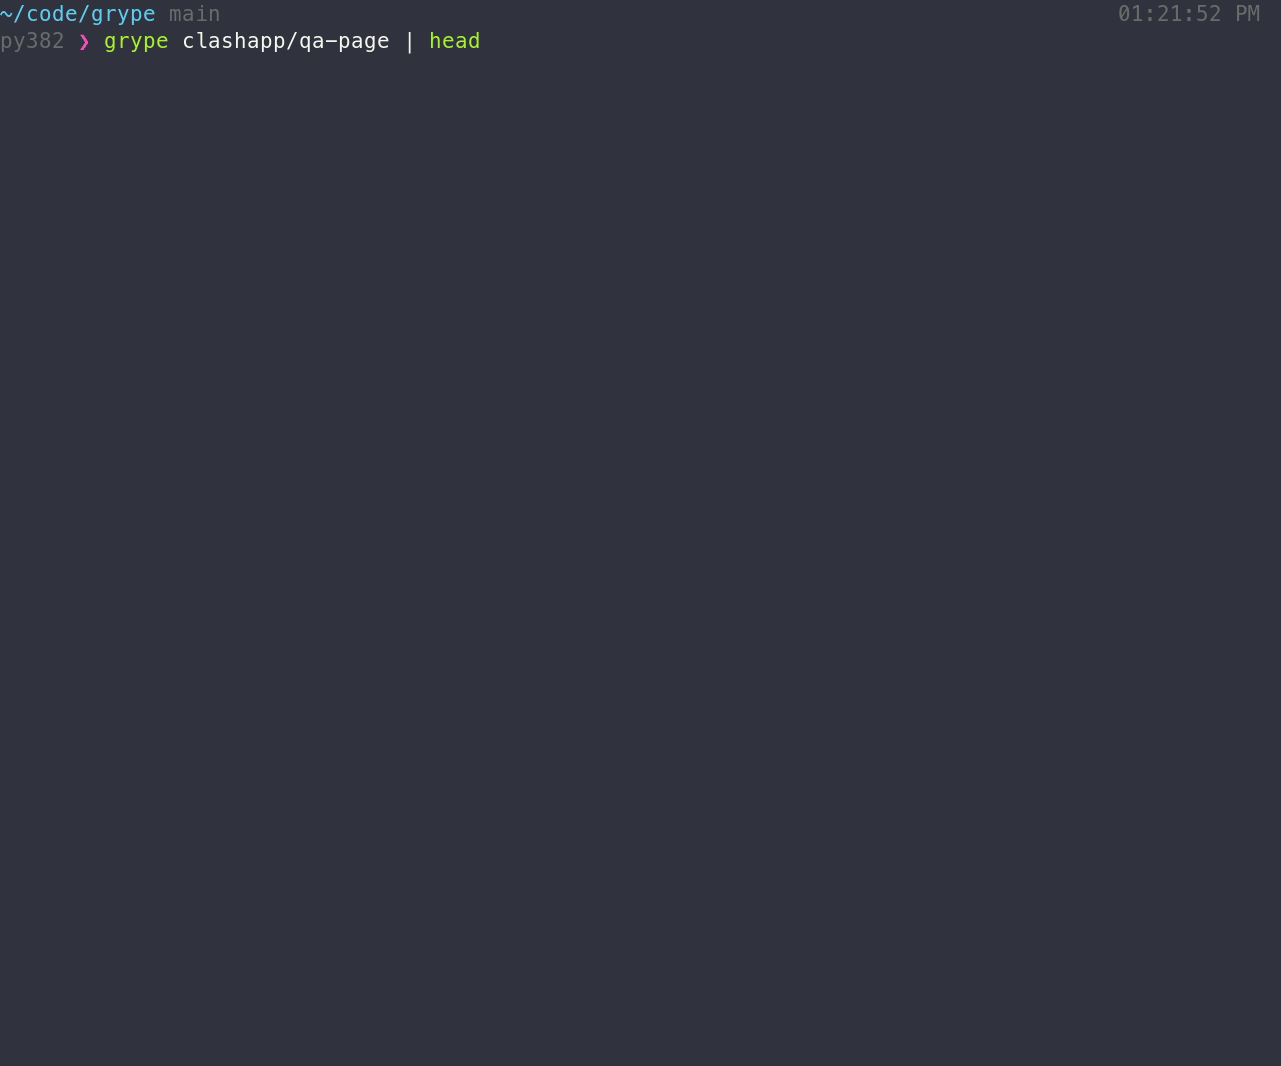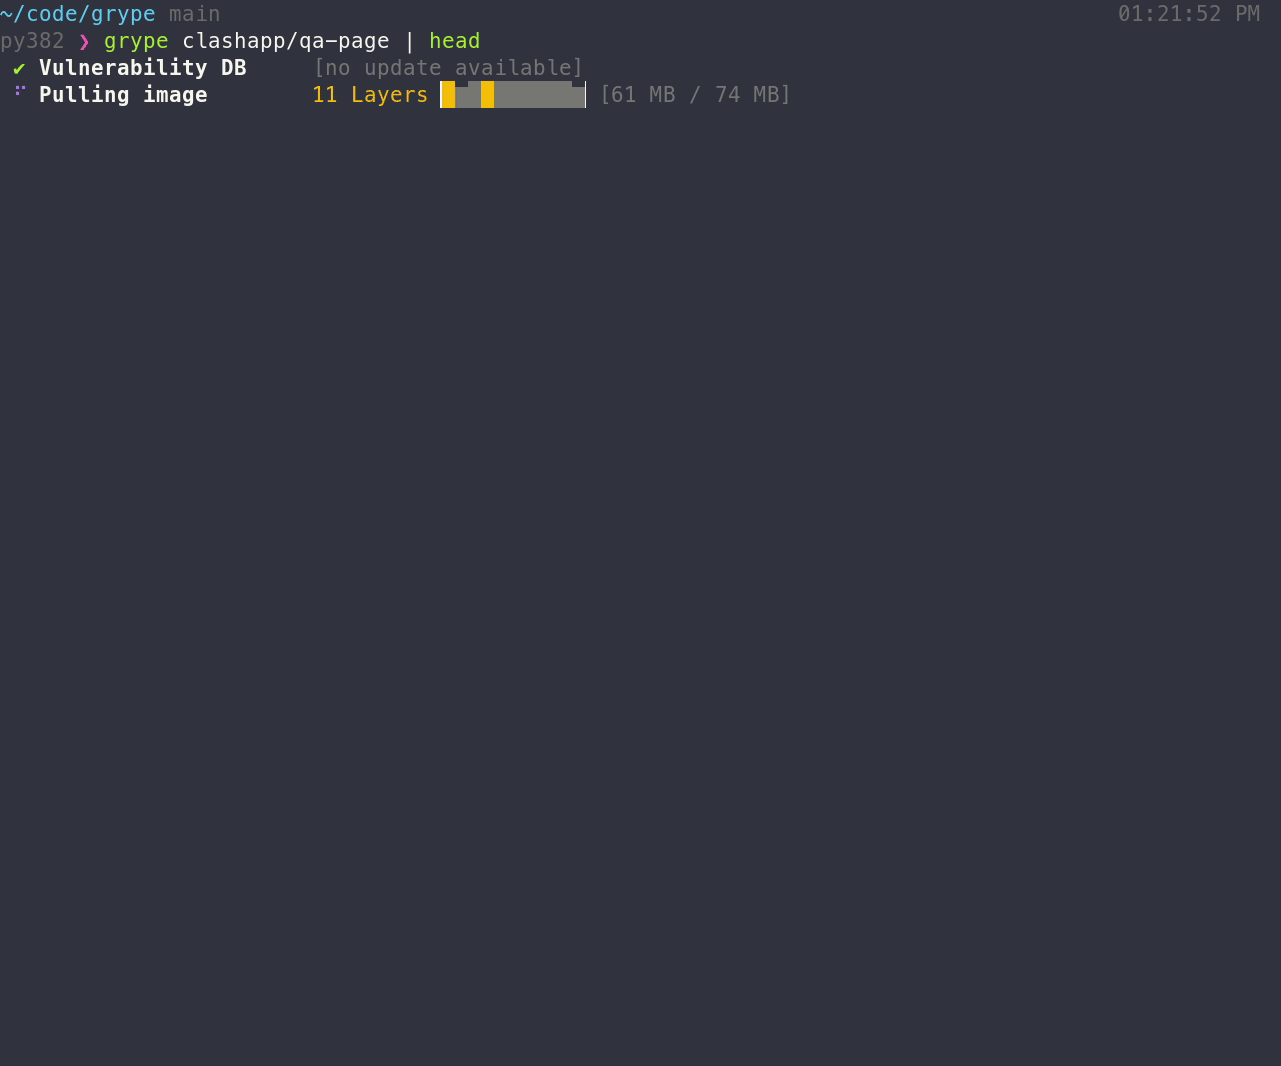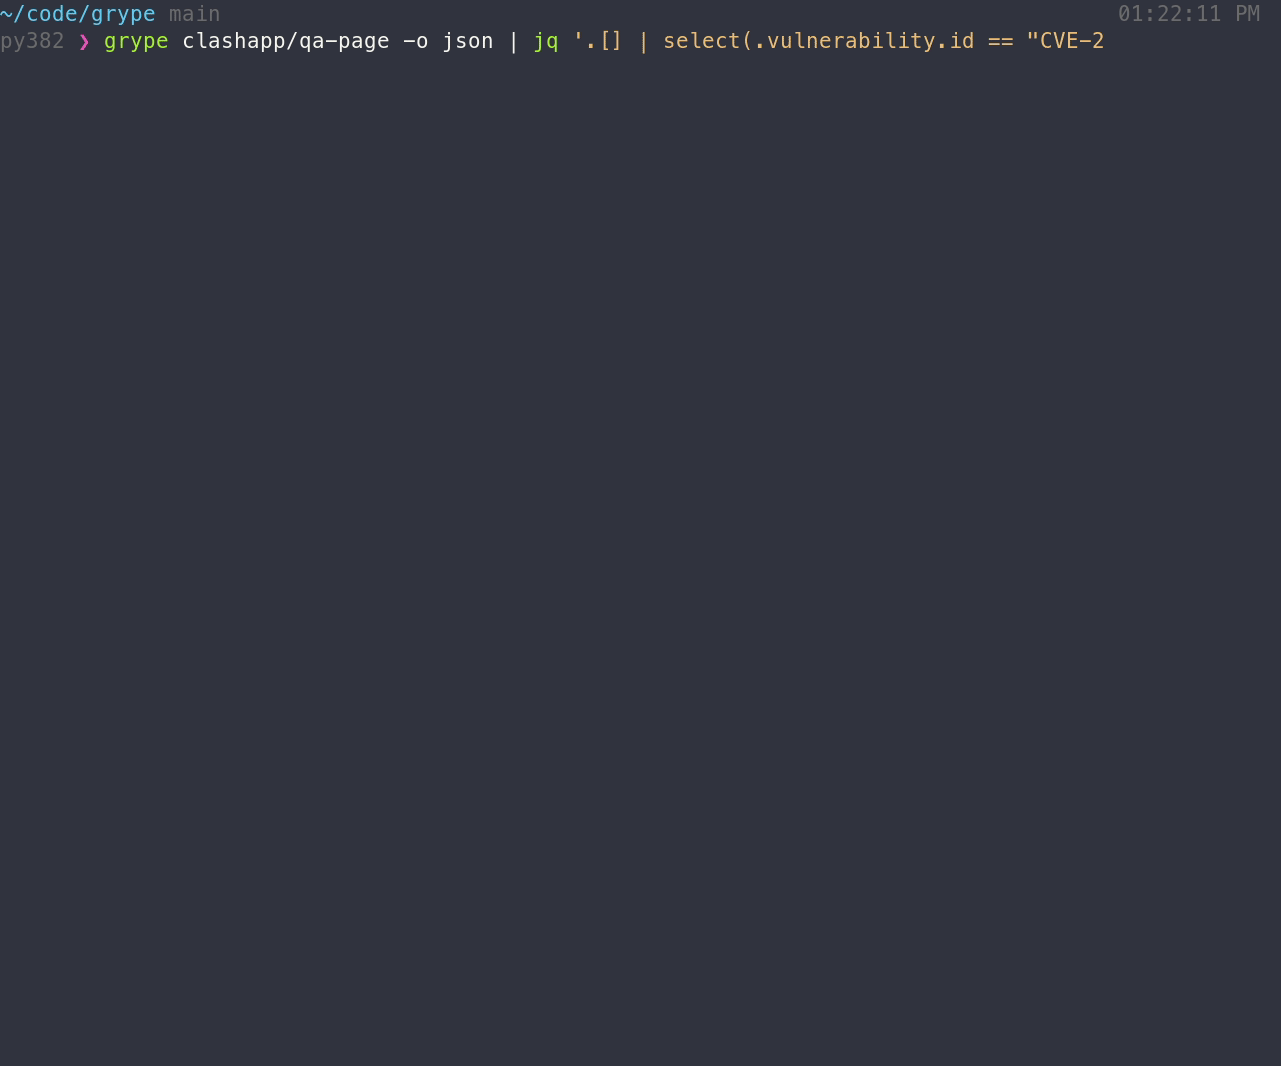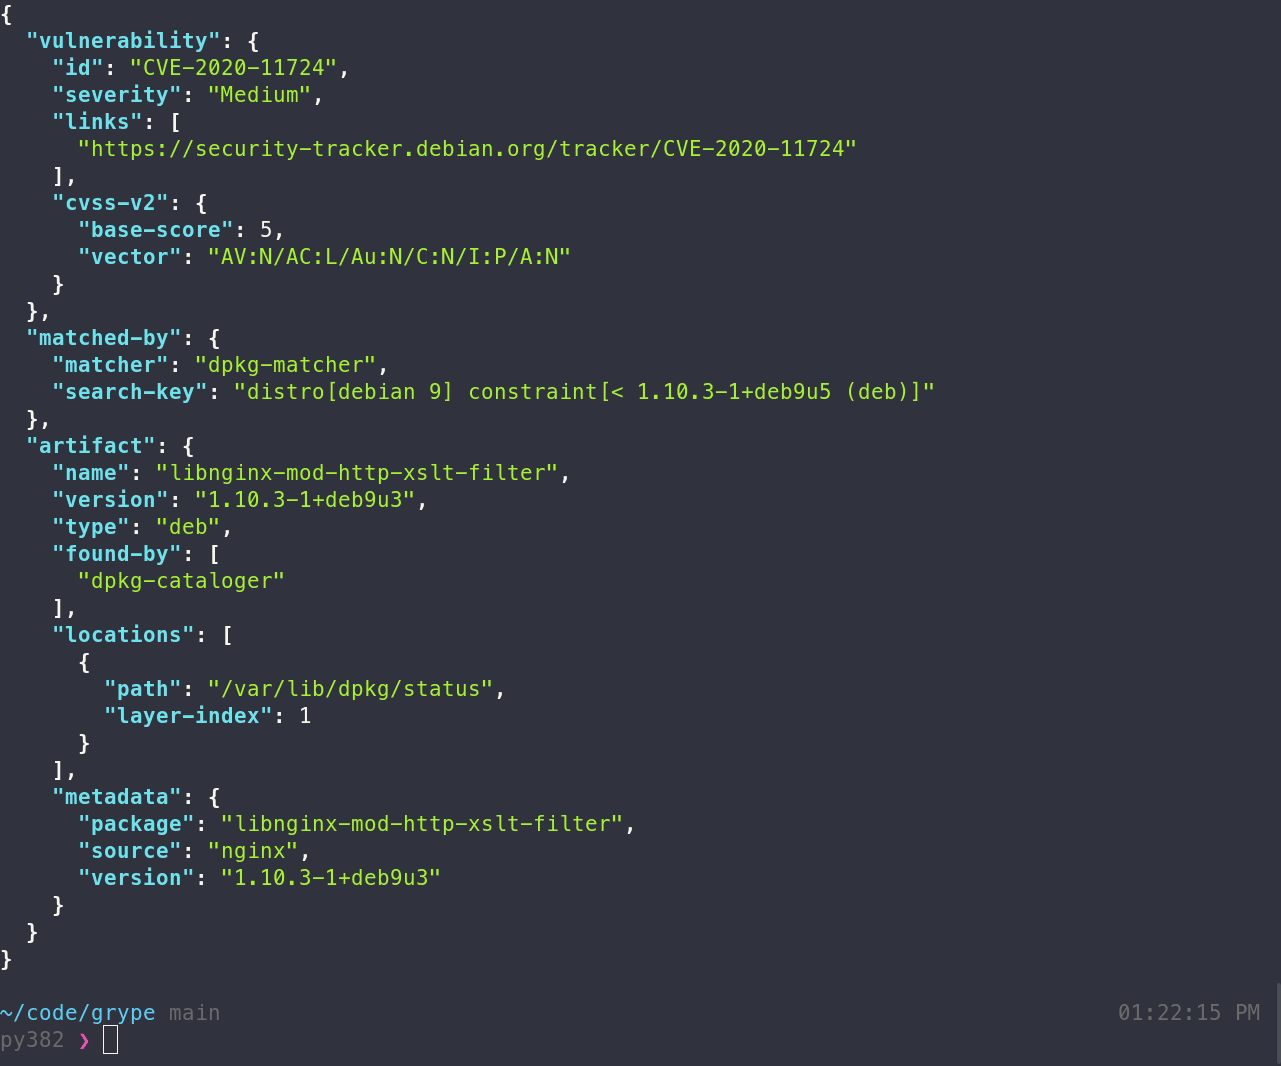
Features
- Scan container images, filesystems, and SBOMs for known vulnerabilities (see the docs for a full list of supported scan targets)
- Supports major OS package ecosystems (Alpine, Debian, Ubuntu, RHEL, Oracle Linux, Amazon Linux, and more)
- Supports language-specific packages (Ruby, Java, JavaScript, Python, .NET, Go, PHP, Rust, and more)
- Supports Docker, OCI, and Singularity image formats
- Threat & risk prioritization with EPSS, KEV, and risk scoring (see interpreting the results docs)
- OpenVEX support for filtering and augmenting scan results
[!TIP] New to Grype? Check out the Getting Started guide for a walkthrough!
Installation
The quickest way to get up and going:
curl -sSfL https://get.anchore.io/grype | sudo sh -s -- -b /usr/local/bin
[!TIP] See Installation docs for more ways to get Grype, including Homebrew, Docker, Chocolatey, MacPorts, and more!
The basics
Scan a container image or directory for vulnerabilities:
# container image
grype alpine:latest

# directory
grype ./my-project
Local containers-storage images
On Linux, grype can scan images from a local containers-storage store (e.g. built with Buildah or Podman) when asked explicitly; plain image references never look there:
grype --from containers-storage localhost/myimage:latest

# rootless stores must be read from inside the builder's user namespace
podman unshare grype --from containers-storage localhost/myimage:latest
This is included in the Linux release binaries. When building from source, add -tags containers_image_openpgp,exclude_graphdriver_btrfs.
Scan an SBOM for even faster vulnerability detection:
# scan a Syft SBOM
grype sbom:./sbom.json

# pipe an SBOM into Grype
cat ./sbom.json | grype
[!TIP] Check out the Getting Started guide to explore all of the capabilities and features.
Want to know all of the ins-and-outs of Grype? Check out the CLI docs and configuration docs.
Contributing
We encourage users to help make these tools better by submitting issues when you find a bug or want a new feature. Check out our contributing overview and developer-specific documentation if you are interested in providing code contributions.
For commercial support options with Syft or Grype, please contact Anchore.
Come talk to us!
The Grype Team holds regular community meetings online. All are welcome to join to bring topics for discussion.
- Check the calendar for the next meeting date.
- Add items to the agenda (join this group for write access to the agenda)
- See you there!
PHP-Parser
nikic·PHP
用 PHP 写的 PHP 解析器,能把源码转成 AST,方便做静态分析、代码改写和工具链开发。
PHP解析器+3代码审计 / SAST
17474+31.1kv5.9.02026-11-05 11:53 UTC
phpstan
phpstan·PHP
PHP 静态分析工具,不用运行代码就能扫出类型错误和潜在 bug,适合在 CI 里给 PHP 项目做质量把关。
静态分析+4代码审计 / SAST
14153+19712.3.52026-11-10 15:52 UTC

PHP-CS-Fixer
PHP-CS-Fixer·PHP
自动检测并修复 PHP 代码风格问题的命令行工具,让团队无需手动调整格式就能统一编码规范。
代码风格+4代码审计 / SAST
13574+11.7kv3.95.302026-11-10 00:13 UTC
syft
anchore·Go
从容器镜像和文件系统生成软件物料清单(SBOM)的 CLI 工具与 Go 库,支持 CycloneDX 和 SPDX 格式,用于摸清镜像里到底装了哪些依赖。
软件物料清单+4代码审计 / SAST
9869+191.0kv1.57.12026-11-09 14:36 UTC