bbot

blacklanternsecurityAGPL-3.0活跃维护

递归式互联网扫描器,面向渗透测试和漏洞赏金场景,自动完成资产发现、攻击面管理与 OSINT 信息收集。

The recursive internet scanner for hackers. 🧡

v3.0.2发布于 2026-08-24 14:31 UTC11,077star +73 / 7 天988fork同步于 2026-11-10 05:29 UTC

怎么上手

从 README 代码块原样提取,可能是其中一种安装方式
pipx install bbot
pipx install --pip-args '\--pre' bbot
硬件要求

README 没有说明硬件要求。

下载:源码 zip·GitHub Releases(安装包)本站不镜像安装包

项目说明

这个项目的说明还在生成中,先参考下面「最近发版」和 README。

最近发版

3 个版本v3.0.2
  1. v3.0.23.0.2最新正式版2026-08-24 · 2026-08-24 14:31 UTC

    Release 3.0.2

    Highlights

    • blasthttp bumped to 0.10.0 (#3385). Response.decode_error is surfaced on HTTP_RESPONSE events and tagged decode-error, so an undecoded body is never treated as content. redirect_cookies now passes through WebHelper.request().
    • New js-audit preset (bbot/presets/web/js-audit.yml). trufflehog streams HTTP bodies via stdin and includes the source URL on findings; its _module_threads is bumped to 2.
    • Test suite parallelized with pytest-xdist (#3353).
    • Fix: custom YARA rules matching but emitting nothing (#3374).
    • Fix: docker_pull crash on a failed registry request.
    • Reinstall module deps when they're missing from the environment (#3338). Adds packaging as a runtime dependency.
    • Raise process pool max_tasks_per_child from 25 to 250 (#3375).
    • CI: pass benchmark refs through env and quote them (#3354).
    • nuclei 3.11.0 to 3.11.1 (#3367); trufflehog 3.95.9 to 3.97.0 (#3376).

    Maintenance

    • Dependabot bumps across the uv and github-actions groups: xxhash 4.0.0, ruff 0.16.2, pre-commit 4.6.2, fastapi 0.141.1, uvicorn 0.52.1, lxml 6.1.1, pip 26.2.1, packaging 26.3, tldextract 5.3.2, websockets 16.1.1, mmh3 5.2.1, orjson 3.11.9, regex 2026.7.19, cachetools 7.1.7, pytest-env 1.7.0, pytest-httpserver 1.1.5, actions/setup-python 7.
  2. v3.0.13.0.12026-07-21 · 2026-07-21 16:17 UTC
    查看更新说明

    Fixes

    • Restore cloudcheck tag propagation to URL / OPEN_TCP_PORT children (#3309). _minimize() was wiping _resolved_hosts on parent events, starving dnsresolve when child events reached it. Cloud tags never made it past the DNS_NAME.
    • Fix virtualhost.finish() crash when the baseline request returned None (#3273).
    • Escape control characters in console output so raw bytes in scan data can't garble the terminal (#3274, closes #3258).
    • Fix stale baddns config key in the kitchen-sink preset; adds a test that validates every bundled preset (#3280, closes #3279).
    • Fix openssl_dev_headers dep check to actually require the header, so minimal images (e.g. python:3.11-slim) no longer skip installing libssl-dev (#3282, closes #3272).
    • Point API-key docs to secrets.yml in the sections that still mentioned bbot.yml (#3283, closes #3270).

    waf_bypass improvements

    • Lower neighbor_cidr default from /24 to /28 (module + waf-bypass preset).
    • Parallelize bypass checks in finish() up to 100 by default.
    • Distinguish direct vs neighbor bypass candidates in log output.
    • Demote non-IP DNS result log from warning to verbose.

    Tooling updates

    • Update nuclei to 3.11.0 (#3275).
    • Update trufflehog to 3.95.9 (#3276, #3295).

    Dependency bumps

    beautifulsoup4 4.14.3→4.15.0, cachetools 6.2.6→7.1.4, cryptography 46.0.5→48.0.1, deepdiff 8.6.1→9.1.0, dnspython 2.7.0→2.8.0, griffe 1.15.0→2.1.0, idna 3.11→3.18, lxml 6.0.2→6.1.0, maturin 1.13.3→1.14.1, mike 2.1.3→2.2.0, mkdocs-material 9.7.1→9.7.7, mkdocstrings 0.30.1→1.0.6, mkdocstrings-python 2.0.2→2.0.5, pip 26.0.1→26.1.2, pre-commit 4.5.1→4.6.0, pydantic 2.12.5→2.13.4, pymdown-extensions 10.20.1→11.0.1, pytest 8.4.2→9.1.1, pytest-cov 7.0.0→7.1.0, pytest-env 1.1.5→1.6.0, pytest-rerunfailures 16.1→16.4, regex 2026.1.15→2026.7.10, requests 2.32.5→2.33.0, ruff 0.15.18→0.15.22, soupsieve 2.8.3→2.8.4, starlette 0.52.1→1.3.1, tornado 6.5.4→6.5.7, urllib3 2.6.3→2.7.0, websockets 15.0.1→16.0, werkzeug 3.1.5→3.1.8, xxhash 3.6.0→3.8.1, ansible-runner 2.4.2→2.4.3, plus actions/cache v5→v6.

    Full changelog: https://github.com/blacklanternsecurity/bbot/compare/v3.0.0...v3.0.1

  3. v3.0.03.0.02026-07-08 · 2026-07-08 15:17 UTC
    查看更新说明

    BBOT 3.0.0

    [!WARNING] Upgrading from 2.x is not drop-in. The CLI, flags, preset syntax, event API, config keys, and module set all changed in backwards-incompatible ways. Read the 2.x to 3.0 migration guide before upgrading. The changes most likely to bite:

    • -s now means --seeds, not --silent (silent moved to -S). A script passing -s for quiet output will now add a seed instead, with no error.
    • --whitelist was retired: -t/--targets now defines scope, and -s/--seeds drives the scan.
    • --allow-deadly was removed, and several flags were renamed (e.g. noisy to loud).
    • Module options are now pydantic-validated; the legacy options dict hard-fails.
    • Some event types, event attributes, and config keys were renamed or removed.

    Highlights

    • New HTTP engine (blasthttp): in-process, rate-limited HTTP replacing the httpx subprocess (#2992, #3021)
    • New DNS engine (BlastDNS) (#3042)
    • Pydantic config + preset validation: typos and type errors are caught before a scan starts (#2486, #3058)
    • Scope rework: clean split between target (scope) and seeds (drivers); --whitelist retired (#2789)
    • Findings and Vulnerabilities unified, with Severity and Confidence (#2436, #2740)
    • asndb: faster ASN enrichment, plus ASNs usable as scan targets (#2957, #2741)
    • Lightfuzz overhaul: new SSRF and ESI submodules, far fewer false positives (#2967)
    • Major performance work: memory and CPU optimizations, bounded DNS caches, HTTP body stripping, string interning (#2953, #3085, #3088)
    • Preset naming / tag standardization across flags, presets, and event tags (#2986)
    • New modules: MongoDB / Elastic / Kafka / RabbitMQ / ZeroMQ / NATS outputs, legba, trajan, virtualhost, waf_bypass, dnsspf, Hetzner bucket
    • Modules removed: wappalyzer, smuggler, digitorus, sitedossier, passivetotal, wpscan

    Core & Packaging

    • Packaging moved from Poetry to uv + hatchling, and supported Python is now 3.10 - 3.14 (#2900, #2731).
    • Config values and presets are validated with pydantic before a scan runs, so typos and wrong types fail fast instead of silently doing nothing. The legacy per-module options dict is no longer accepted (#2486, #3058, #3119).
    • Malformed YAML in a config or preset now produces a readable error instead of a stack trace (#3159).
    • New --reset-config / --reset-secrets to regenerate stale config files (#3240).

    Scope & Targeting

    • Scope was reworked around a target/seeds split: -t/--targets defines scope, -s/--seeds supplies the starting events, --whitelist is gone, and --strict-scope now means "this exact host only" (#2789).
    • ASNs can be used directly as scan targets (#2741).
    • Files can be passed as targets, seeds, or blacklist entries inside presets, and target lists may contain comments (#2996, #3031).

    HTTP & Web

    • All web traffic now runs in-process through one shared, rate-limited client (blasthttp) instead of a separate httpx subprocess (#2992, #3021).
    • HTTP wildcard/catch-all host detection cuts false positives on servers that answer every request (#3164).
    • 429 Too Many Requests responses are now honored for rate limiting (#3145).
    • HTTP timeout settings were consolidated into one place (#3222).
    • SSL verification was split so BBOT verifies its own infrastructure calls by default while still not verifying untrusted target traffic (#3186).

    DNS

    • New DNS resolution engine, BlastDNS (#3042).
    • Fixed the DNS brute-force canary check, which was silently non-functional (#3005).
    • SPF records now yield the IPs and CIDRs they authorize (#3144).
    • Better graph fidelity for shared infrastructure, and noisy PTR floods are collapsed / filtered by default (#3141, #3115, #3039).

    Findings & Output

    • Findings and Vulnerabilities are now a single event type carrying Severity and Confidence

用户点评

登录用户的真实使用记录,可按版本和硬件筛选
共 0 条

    还没有人点评。第一个说出真实体验的人最有价值。

    README 原文

    未翻译

    bbot_banner

    Python Version License PyPi Downloads Ruff Tests Codecov Discord

    BEE·bot is a multipurpose scanner inspired by Spiderfoot, built to automate your Recon, Bug Bounties, and ASM!

    https://github.com/blacklanternsecurity/bbot/assets/20261699/e539e89b-92ea-46fa-b893-9cde94eebf81

    A BBOT scan in real-time - visualization with VivaGraphJS

    Installation

    # stable version
    pipx install bbot
    
    # bleeding edge (dev branch)
    pipx install --pip-args '\--pre' bbot
    

    For more installation methods, including Docker, see Getting Started

    Upgrading from 2.x? BBOT 3.0 contains breaking changes to the CLI, presets, modules, events, and Python API. See the 2.x → 3.0 Migration Guide (source) before upgrading.

    Speed tip: BBOT's DNS resolver (blastdns) spins up multiple threads per resolver in /etc/resolv.conf. Adding more unfiltered resolvers dramatically speeds up scans. See the sample resolv.conf and Tips and Tricks for details.

    Example Commands

    1) Subdomain Finder

    Passive API sources plus a recursive DNS brute-force with target-specific subdomain mutations.

    # find subdomains of evilcorp.com
    bbot -t evilcorp.com -p subdomain-enum
    
    # passive sources only
    bbot -t evilcorp.com -p subdomain-enum -rf passive
    
    description: Enumerate subdomains via APIs, brute-force
    
    flags:
      # enable every module with the subdomain-enum flag
      - subdomain-enum
    
    output_modules:
      # output unique subdomains to TXT file
      - subdomains
    
    config:
      dns:
        threads: 25
        brute_threads: 1000
      # put your API keys here
      # modules:
      #   github:
      #     api_key: ""
      #   chaos:
      #     api_key: ""
      #   securitytrails:
      #     api_key: ""


    BBOT consistently finds 20-50% more subdomains than other tools. The bigger the domain, the bigger the difference. To learn how this is possible, see How It Works.

    subdomain-stats-ebay

    2) Web Spider

    # crawl evilcorp.com, extracting emails and other goodies
    bbot -t evilcorp.com -p spider
    
    description: Recursive web spider
    
    modules:
      - http
    
    blacklist:
      # Prevent spider from invalidating sessions by logging out
      - "RE:/.*(sign|log)[_-]?out"
    
    config:
      web:
        # how many links to follow in a row
        spider_distance: 2
        # don't follow links whose directory depth is higher than 4
        spider_depth: 4
        # maximum number of links to follow per page
        spider_links_per_page: 25


    3) Email Gatherer

    # quick email enum with free APIs + scraping
    bbot -t evilcorp.com -p email-enum
    
    # pair with subdomain enum + web spider for maximum yield
    bbot -t evilcorp.com -p email-enum subdomain-enum spider
    
    description: Enumerate email addresses from APIs, web crawling, etc.
    
    flags:
      - email-enum
    
    output_modules:
      - emails


    4) Web Scanner

    # run a light web scan against www.evilcorp.com
    bbot -t www.evilcorp.com -p web
    
    # run a heavy web scan against www.evilcorp.com
    bbot -t www.evilcorp.com -p web-heavy
    
    description: Quick web scan
    
    include:
      - iis-shortnames
    
    flags:
      - web
    
    
    description: Aggressive web scan
    
    include:
      # include the web preset
      - web
    
    flags:
      - web-heavy


    5) Everything Everywhere All at Once

    # everything everywhere all at once
    bbot -t evilcorp.com -p kitchen-sink
    
    # roughly equivalent to:
    bbot -t evilcorp.com -p subdomain-enum cloud-enum code-enum email-enum spider web paramminer webbrute web-screenshots
    
    description: Everything everywhere all at once
    
    include:
      - subdomain-enum
      - cloud-enum
      - code-enum
      - email-enum
      - spider
      - web
      - paramminer
      - webbrute
      - web-screenshots
      - baddns-heavy
    
    config:
      modules:
        dnsbrute:
          recursive_mutations: true
        dnscommonsrv:
          recursive_mutations: true
        webbrute:
          avoid_wafs: False
        wayback:
          urls: True
          parameters: True
          archive: True


    How it Works

    Click the graph below to explore the inner workings of BBOT.

    image

    Output Modules

    ...and more!

    BBOT as a Python Library

    Synchronous
    from bbot.scanner import Scanner
    
    if __name__ == "__main__":
        scan = Scanner("evilcorp.com", presets=["subdomain-enum"])
        for event in scan.start():
            print(event)
    
    Asynchronous
    from bbot.scanner import Scanner
    
    
    async def main():
        scan = Scanner("evilcorp.com", presets=["subdomain-enum"])
        async for event in scan.async_start():
            print(event.json())
    
    
    if __name__ == "__main__":
        import asyncio
    
        asyncio.run(main())
    

    A BBOT Discord Bot that responds to the /scan command. Scan the internet from the comfort of your discord server!
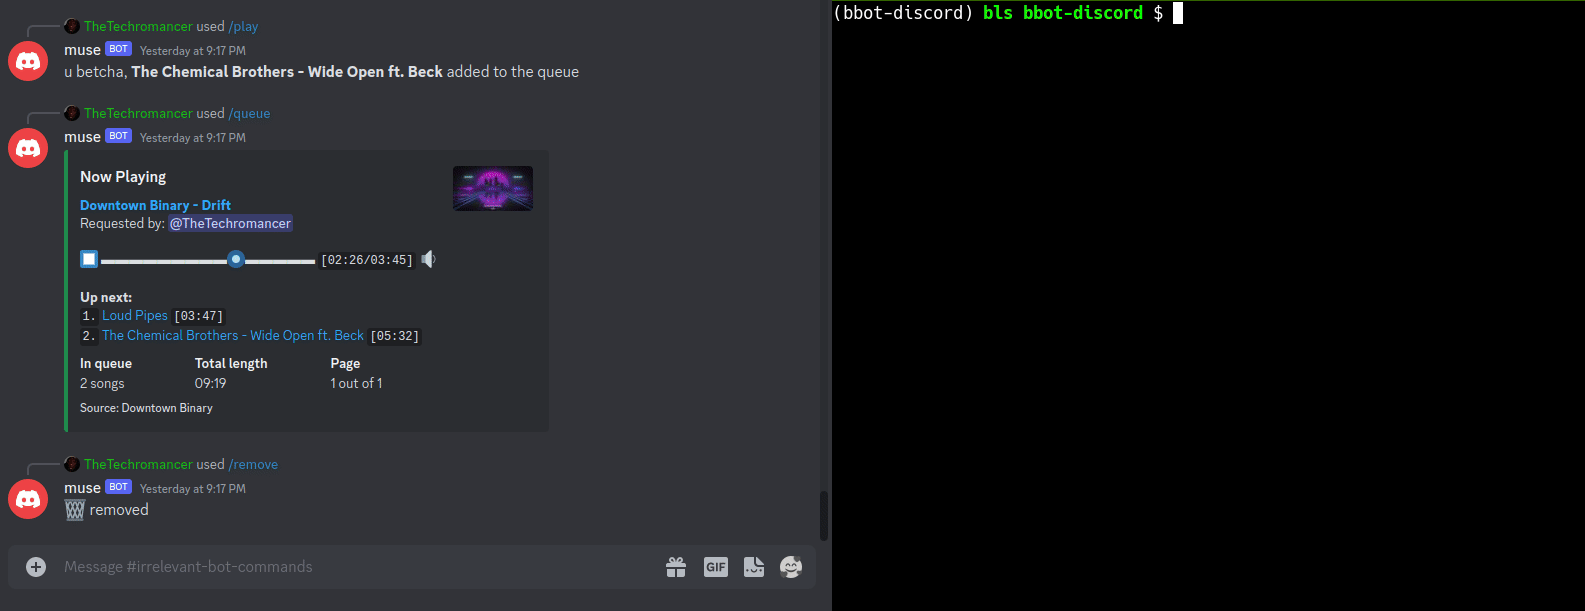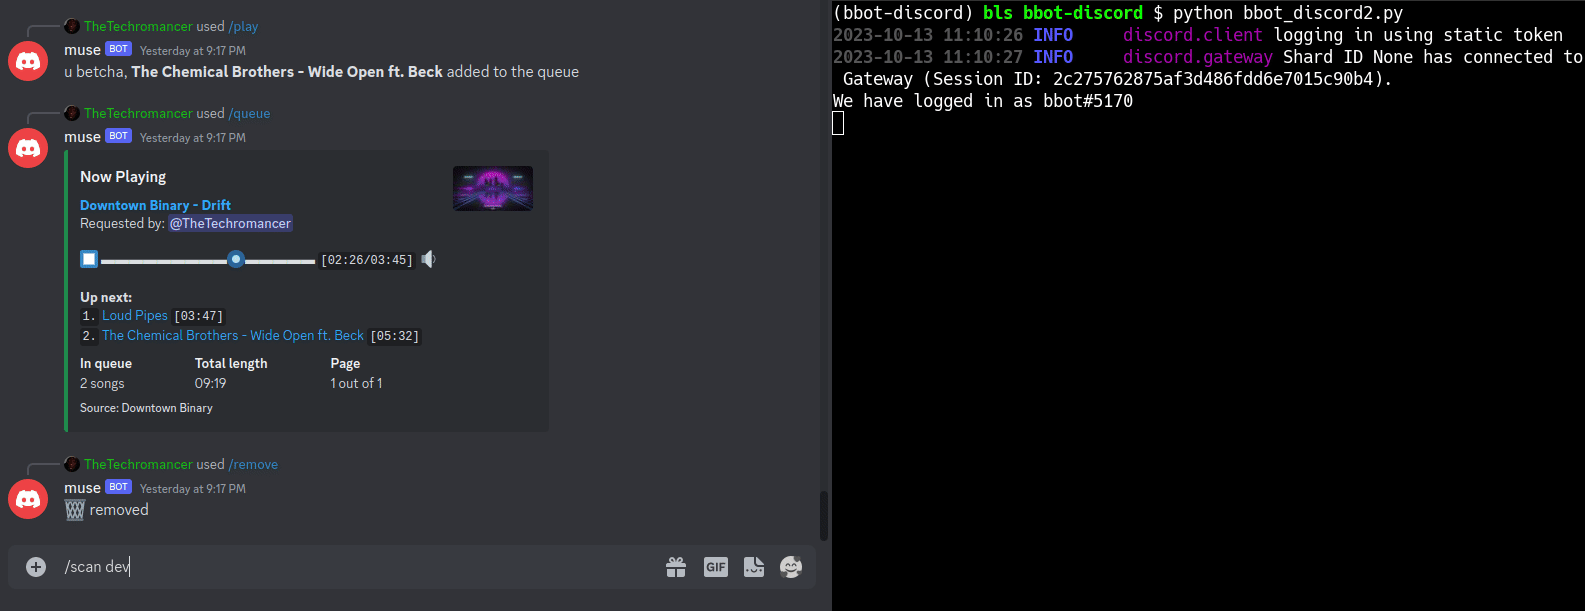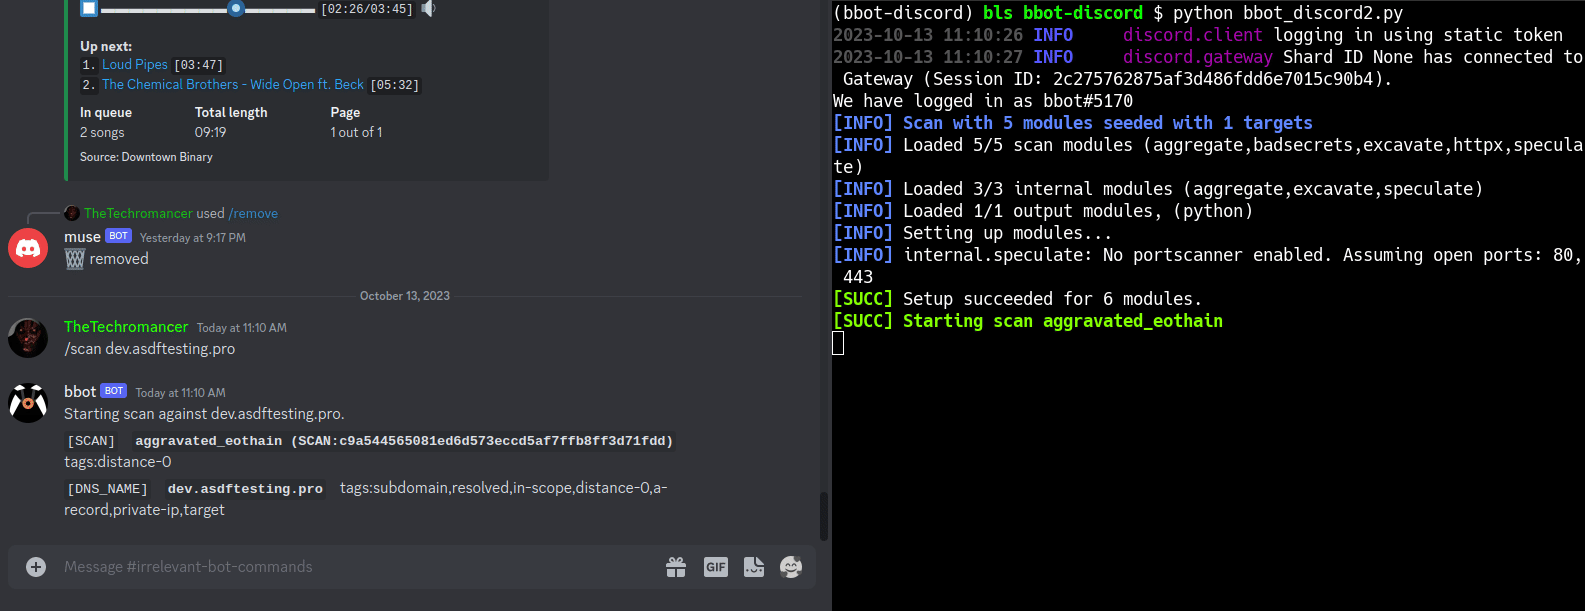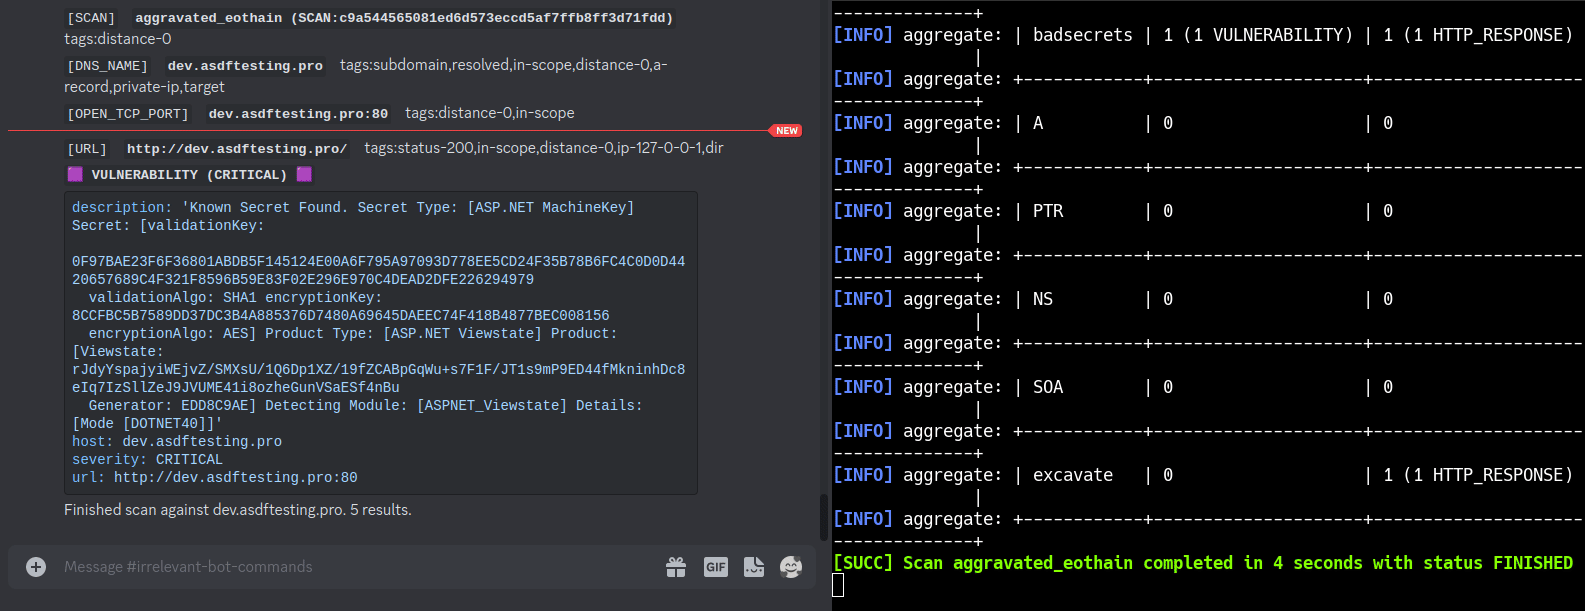
    bbot-discord

    Feature Overview

    • Support for Multiple Targets
    • Web Screenshots
    • Suite of Offensive Web Modules
    • NLP-powered Subdomain Mutations
    • Native Output to Neo4j (and more)
    • Automatic dependency install with Ansible
    • Search entire attack surface with custom YARA rules
    • Python API + Developer Documentation

    Targets

    BBOT accepts an unlimited number of targets via -t. You can specify targets either directly on the command line or in files (or both!):

    bbot -t evilcorp.com evilcorp.org 1.2.3.0/24 -p subdomain-enum
    

    Targets can be any of the following:

    • DNS Name (evilcorp.com)
    • IP Address (1.2.3.4)
    • IP Range (1.2.3.0/24)
    • Open TCP Port (192.168.0.1:80)
    • URL (https://www.evilcorp.com)
    • Email Address ([email protected])
    • Organization (ORG:evilcorp)
    • Username (USER:bobsmith)
    • Filesystem (FILESYSTEM:/tmp/asdf)
    • Mobile App (MOBILE_APP:https://play.google.com/store/apps/details?id=com.evilcorp.app)

    For more information, see Targets. To learn how BBOT handles scope, see Scope.

    API Keys

    Similar to Amass or Subfinder, BBOT supports API keys for various third-party services such as SecurityTrails, etc.

    The standard way to do this is to enter your API keys in ~/.config/bbot/secrets.yml. Note that multiple API keys are allowed:

    modules:
      shodan_dns:
        api_key: 4f41243847da693a4f356c0486114bc6
      c99:
        # multiple API keys
        api_key:
          - 21a270d5f59c9b05813a72bb41707266
          - ea8f243d9885cf8ce9876a580224fd3c
          - 5bc6ed268ab6488270e496d3183a1a27
      virustotal:
        api_key: dd5f0eee2e4a99b71a939bded450b246
      securitytrails:
        api_key: d9a05c3fd9a514497713c54b4455d0b0
    

    If you like, you can also specify them on the command line:

    bbot -c modules.virustotal.api_key=dd5f0eee2e4a99b71a939bded450b246
    

    For details, see Configuration.

    Complete Lists of Modules, Flags, etc.

    Documentation

    Contribution

    Some of the best BBOT modules were written by the community. BBOT is being constantly improved; every day it grows more powerful!

    We welcome contributions. Not just code, but ideas too! If you have an idea for a new feature, please let us know in Discussions. If you want to get your hands dirty, see Contribution. There you can find setup instructions and a simple tutorial on how to write a BBOT module. We also have extensive Developer Documentation.

    Thanks to these amazing people for contributing to BBOT! :heart:

    Special thanks to:

    • @TheTechromancer for creating BBOT
    • @liquidsec for his extensive work on BBOT's web hacking features, including badsecrets and baddns
    • Steve Micallef (@smicallef) for creating Spiderfoot
    • @kerrymilan for his Neo4j and Ansible expertise
    • @domwhewell-sage for his family of badass code-looting modules
    • @aconite33 and @amiremami for their ruthless testing
    • Aleksei Kornev (@alekseiko) for granting us ownership of the bbot Pypi repository <3