README 未给出具体用法,安装与使用步骤需查阅官方文档 docs.zizmor.sh;README 未说明默认配置与退出码行为
zizmor
zizmorcoreMIT活跃维护用 Rust 写的 GitHub Actions 静态分析工具,能提前发现工作流里的安全漏洞和配置问题,避免 CI 被利用。
Static analysis for GitHub Actions (and more)
v1.32.0发布于 2026-11-02 23:57 UTC6,964star +31 / 7 天280fork同步于 2026-11-10 23:34 UTC
静态分析 CI/CD 配置的 Rust 工具,专查 GitHub Actions 工作流里的安全漏洞
用 Rust 写的 GitHub Actions 静态分析工具,能提前发现工作流里的安全漏洞和配置问题,避免 CI 被利用。
核心能力
- 检测模板注入导致的攻击者代码执行
- 发现凭证意外持久化与泄露
- 识别过宽权限范围与凭据授予
- 识别冒名提交与易混淆的 git 引用
- 覆盖 GitHub Actions、Dependabot 与 pre-commit
容易踩的坑
内容由模型根据 README 生成,可能不完整或不准确,以官方文档为准。看原文 README
- v1.32.0最新正式版2026-11-02 · 2026-11-02 23:57 UTC
New Features 🌈🔗
- zizmor now has experimental support for GitHub Actions workflow lockfiles. Please see the limitations documentation for more information about the current implementation and its limitations (#2463)
Enhancements 🌱🔗
-
zizmor's input collection is now "root-aware" by default, meaning that invocations like zizmor . will no longer collect inputs unless they would actually be used by GitHub Actions, etc. This should eliminate spurious findings from (e.g.) workflow definitions in vendored directories. See the input collection documentation for more information. (#2454)
-
zizmor's LSP now honors the didChangeWorkspaceFolders event (#2461)
-
zizmor's LSP now audits pre-commit inputs (#2485)
-
zizmor now provides Windows ARM64 wheels on PyPI (#2424)
Many thanks to @ndabas for proposing and implementing this improvement!
Bug Fixes 🐛🔗
-
Fixed a bug where the bot-conditions audit did not properly flag if: condition of jobs that call a reusable workflow (#2457)
-
Fixed a bug where the obfuscation audit would incorrectly flag (and suggest an incorrect auto-fix for) expressions that constant-reduce to other expressions (#2483)
-
Fixed a bug where the template-injection audit did not flag attacker-controllable contexts wrapped in fromJSON(...), such as fromJSON(toJSON(github.event.issue.title)) (#2495)
-
Fixed a bug where the template-injection audit did not flag attacker-controllable contexts in the values of case(...), such as case(cond, github.event.issue.title, 'x') (#2504)
-
Fixed a class of bugs in the obfuscation audit where a constant-reducible subexpression would not be replaced with a contextually correct form (#2483)
-
Fixed a bug where zizmor would incorrectly audit pre-commit inputs that ended with .yml, despite pre-commit requiring the .yaml suffix (#2485)
-
Fixed a bug where zizmor would not honor some ignore comments for the stale-action-refs audit (#2494)
-
Fixed a bug where zizmor would not honor some ignore comments for the ref-version-mismatch audit (#2494)
- v1.31.12026-10-15 · 2026-10-15 23:16 UTC
查看更新说明
Bug Fixes 🐛🔗
- Fixed a regression in 1.31.0 where some ignore comments/configurations would no longer apply to the dangerous-triggers audit (#2450)
- v1.31.02026-10-15 · 2026-10-15 04:04 UTC
查看更新说明
Enhancements 🌱🔗
-
The typosquat-uses audit now supports pre-commit config inputs (#2437)
-
The self-hosted-runner audit is now significantly more precise (#2350)
Many thanks to @ubiratansoares for proposing and implementing this enhancement!
-
The dangerous-triggers audit now considers the issue_comment trigger fundamentally dangerous (#2396)
-
zizmor is now aware of the image_version workflow trigger (#2397)
-
The dangerous-triggers audit now produces more precise finding/diagnostic spans (#2402)
-
The cache-poisoning audit is now aware of pnpm/setup (#2409)
-
The unpinned-images audit now produces more precise findings when the user's workflow contains an indirect matrix (#2395)
Many thanks to @ubiratansoares for proposing and implementing this enhancement!
-
The cache-poisoning audit is now aware of GitHub's new cache-mode: setting, and will skip any findings that would occur when a job has an effective cache-mode: none (#2418)
-
The cache-poisoning audit now flags usages of cache-mode: write and cache-mode: write-only with dangerous triggers, i.e. triggers that give an attacker privileged code execution (#2426)
-
zizmor now uses a tree-sitter grammar for PowerShell that's more precise/capable of capturing more non-trivial PowerShell expressions (#2444)
Bug Fixes 🐛🔗
-
Fixed a class of false positives/imprecisions in adhoc-packages that caused some pnpm and yarn invocations to be misclassified as package installations (#2386)
Many thanks to @marcalexiei for implementing this improvement!
-
Fixed a bug where zizmor would fail to honor Git submodules and worktrees when discovering configuration files relative to a repo root (#2390)
-
Fixed a bug where the ref-version-mismatch audit would crash on unusually placed version comments (#2394)
-
Fixed a bug where zizmor would fail to handle some pre-commit inputs that use prek extensions to the language_version and default_language_version keys (#2413)
-
Fixed a bug where the use-trusted-publishing audit would fail to detect certain true-positive patterns inside of PowerShell blocks (#2444)
-
- v1.30.12026-09-09 · 2026-09-09 05:34 UTC
查看更新说明
Bug Fixes 🐛🔗
-
Fixed a bug where zizmor would crash on pre-commit inputs that reference a GitHub URL with an explicit .git suffix (#2363)
-
Fixed a bug where self-repository auto-fixes were incorrectly marked as "safe" instead of "unsafe" (#2373)
-
- v1.30.02026-08-30 · 2026-08-30 21:29 UTC
查看更新说明
New Features 🌈🔗
-
New audit: self-repository detects usages of the old "workspace-relative" form for local reusable workflows and actions and recommends the new "self-repository" form instead (#2271) Enhancements 🌱🔗
-
The impostor-commit audit now supports pre-commit config inputs (#2256)
-
The forbidden-uses audit now supports pre-commit config inputs (#2263)
-
The adhoc-packages audit now detects more ad-hoc package management patterns, including bundle add and yarn add
Many thanks to @connorshea for proposing and implementing this enhancement!
-
The archived-uses audit now supports pre-commit config inputs (#2272)
-
The ref-confusion audit now supports pre-commit config inputs (#2274)
-
The cache-poisoning audit now produces more detailed and more precise diagnostics (#2330)
-
The cache-poisoning audit now handles and exposes auto-fixes in a more general manner (#2332)
-
zizmor now recognizes sethvargo/ratchet version comments when evaluating ref pinning (#2319)
Many thanks to @njgudman for proposing and implementing this enhancement!
-
The unpinned-tools audit now produces more detailed and more precise diagnostics (#2339)
-
The unpinned-tools audit now detects usages of extractions/setup-just (#2339)
-
The unpinned-tools audit now detects usages of extractions/setup-crate (#2340)
-
The archived-uses audit now detects several more archived repositories (#2340)
-
The ref-version-mismatch audit now supports uses: that reference reusable workflows (#2344)
-
The stale-action-refs audit now supports uses: that reference reusable workflows (#2345)
Bug Fixes 🐛🔗
-
Fixed a bug where zizmor would reject a .pre-commit-config.yml input containing a prek-specific builtin section (#2259)
-
Fixed a bug where the unpinned-uses audit would fail to honor ignore comments within the same step scope (#2289)
-
Fixed a bug where zizmor would reject a dependabot.yml containing a goproxy-server regist
-
用户点评
登录用户的真实使用记录,可按版本和硬件筛选共 0 条
还没有人点评。第一个说出真实体验的人最有价值。
🌈 zizmor




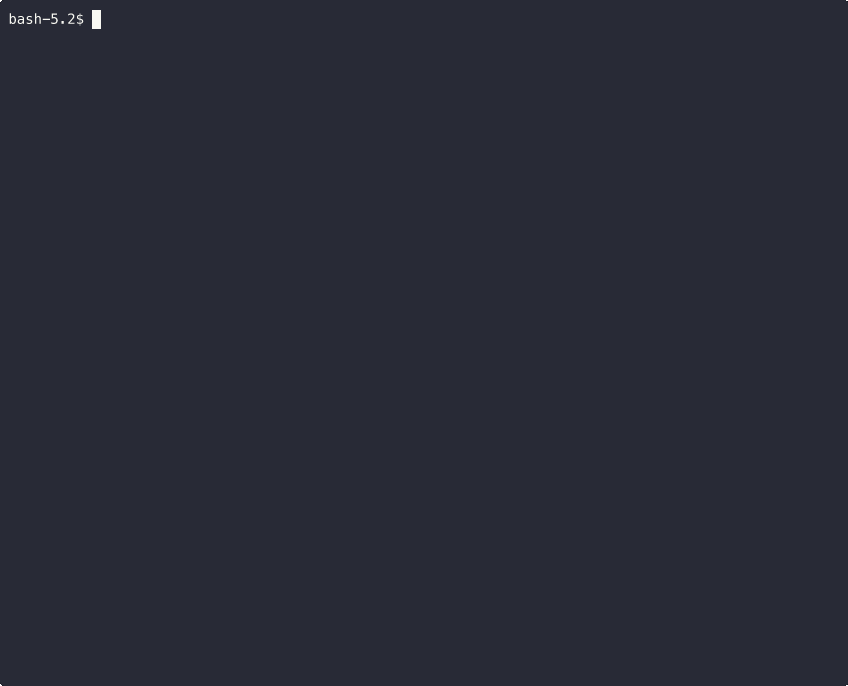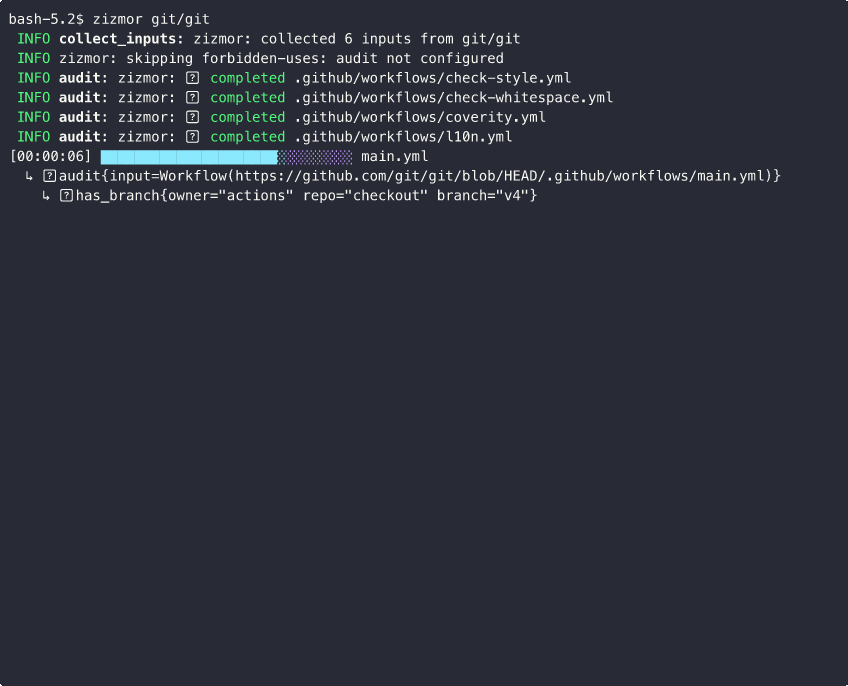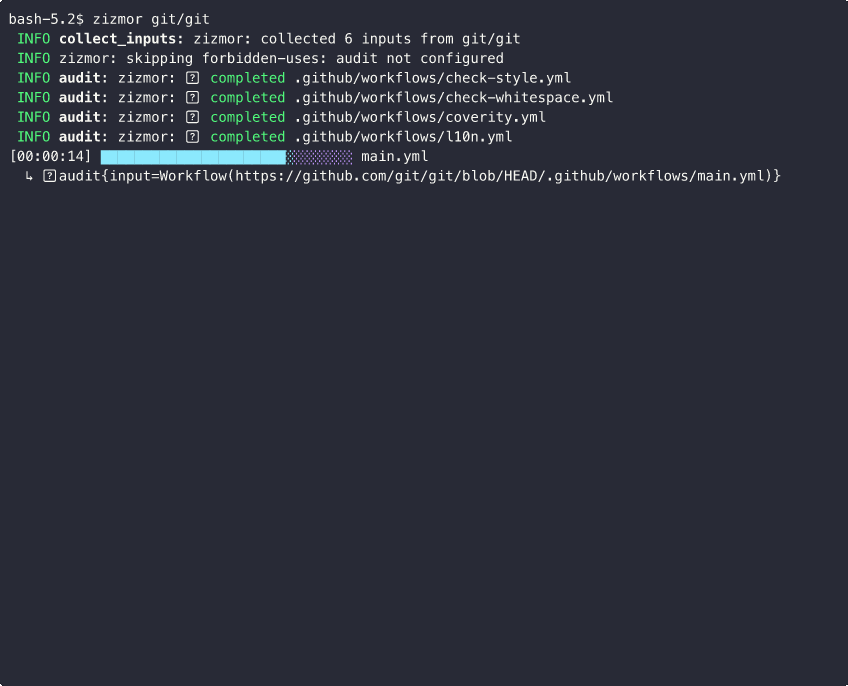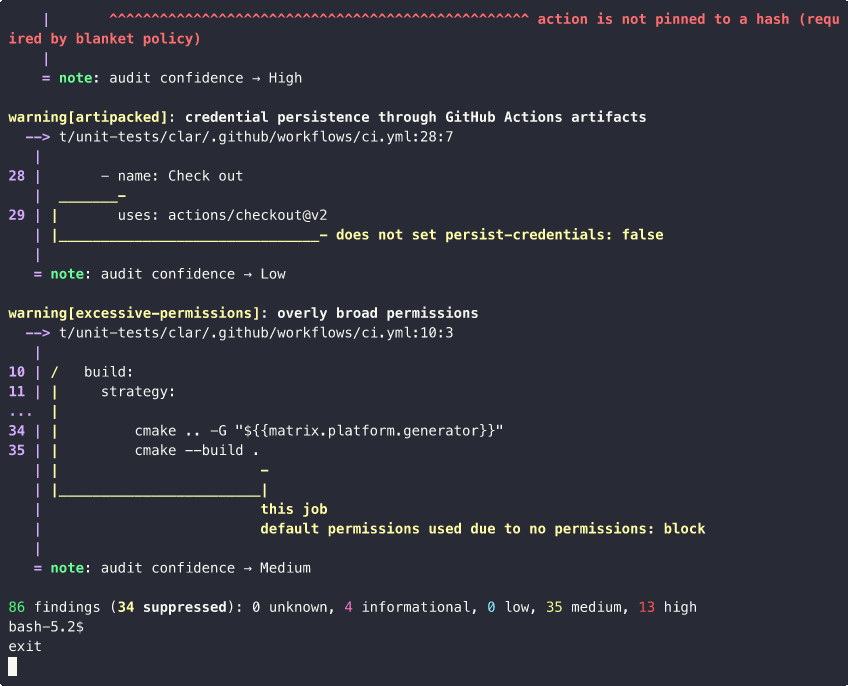
zizmor is a static analysis tool for CI/CD systems.
It can find and fix security issues in common CI/CD setups, including GitHub Actions,
Dependabot, and pre-commit. Some of the things zizmor finds:
- Template injection vulnerabilities, leading to attacker-controlled code execution
- Accidental credential persistence and leakage
- Excessive permission scopes and credential grants to runners
- Impostor commits and confusable
gitreferences - ...and much more!
See zizmor's documentation
for installation steps, as well as a quickstart and
detailed usage recipes.
License
zizmor is licensed under the MIT License.
Contributing
The name?
Now you can have beautiful clean workflows!
Sponsors
zizmor's development is supported by these amazing sponsors!
Want to see your name or logo above? Consider becoming a sponsor through one of the following:
- GitHub Sponsors (preferred)
- thanks.dev
- ko-fi
Star History

Awesome-Hacking
Hack-with-Github
面向黑客、渗透测试员和安全研究员的资源合集,把漏洞赏金、模糊测试、逆向工程等方向的优质清单汇总在一起,方便按需查找学习资料和工具。
渗透测试+4渗透测试 / 漏洞
125193+32511k2026-10-27 01:45 UTC

ImHex
WerWolv·C++
面向逆向工程师和程序员的十六进制编辑器,内置模式语言解析二进制文件结构,支持数据分析、反汇编和取证,深夜使用也不刺眼。
十六进制编辑器+4渗透测试 / 漏洞
55818+552.6kv1.38.12026-10-09 00:56 UTC

x64dbg
x64dbg·C++
Windows 平台的开源用户态调试器,专为逆向工程和恶意软件分析优化,支持反汇编、动态调试和漏洞利用开发。
调试器+4渗透测试 / 漏洞
50270+392.9k2026.05.272026-11-09 10:38 UTC
SkillSpector
NVIDIA·Python
安装前扫描 Claude Code、Codex 和 MCP 技能的安全工具,能发现漏洞、恶意模式、提示注入、数据外泄和供应链风险。
安全扫描+4渗透测试 / 漏洞
25212+3872.2kv2.13.42026-11-10 20:30 UTC